75only - Ends in 0d 00h 00m 00s - Coupon code = 75only
Pass the Fortinet Network Security Expert NSE5_FNC_AD_7.6 Questions and answers with Dumpstech
Exam NSE5_FNC_AD_7.6 Premium Access
View all detail and faqs for the NSE5_FNC_AD_7.6 exam
Refer to the exhibit.
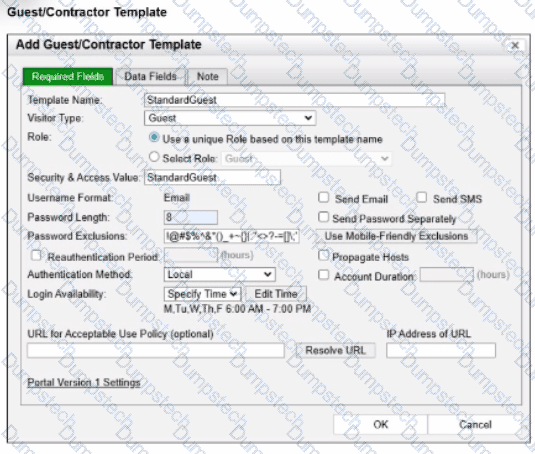
What will happen to the host of a guest user created from this template if the time of connection is 8:00 PM?
Options:
The host will be marked as non-authenticated.
The host will be marked as a rogue device.
The host will be marked as at-risk.
The host will be administratively disabled.
In FortiNAC-F, theGuest & Contractor Templateis a configuration object that defines the parameters for accounts created by sponsors or through self-registration. One of the critical security controls within this template is theLogin Availabilitysetting. This setting restricts the specific days and times during which a guest or contractor is permitted to authenticate and access the network.
As shown in the exhibit, the "StandardGuest" template hasLogin Availabilityset to"Specify Time", with a schedule defined asMon-Fri, 6:00 AM to 7:00 PM. If a guest user attempts to connect or authenticate at8:00 PM, which is outside of the permitted window, FortiNAC-F's policy engine will automatically deny the authentication request. When an authentication attempt is denied due to schedule restrictions, the system does not move the host into the "Authenticated" or "Registered" state required for production access. Instead, the host ismarked as non-authenticatedin the adapter or host view.
This behavior ensures that even if a guest possesses valid credentials, their access is strictly bound by the organizational policy for visitor hours. The host will typically remain in its current isolation or registration VLAN, and the user will see a message on the captive portal indicating that their account is not currently authorized for login. It is important to distinguish this from "at-risk" (C), which relates to security scan failures, or "rogue" (B), which typically refers to unknown devices that have not yet been associated with a valid account or profiling rule.
"Login Availabilitydefines the timeframe during which the guest or contractor account is valid for network access. This schedule is enforced at the time of authentication. If a user attempts to log in outside of the designated window, the authentication is rejected by the system. Consequently, the host record will reflect anon-authenticatedstatus, and the device will remain restricted to the isolation or registration network until a valid login window is reached." —FortiNAC-F Administration Guide: Guest and Contractor Templates Section.
A healthcare organization is integrating FortiNAC-F with its existing MDM. Communication is failing between the systems.
What could be a probable cause?
Options:
Security Fabric traffic is failing
SSH communication is failing
REST API communication is failing
SOAP API communication is failing
The integration between FortiNAC-F and Mobile Device Management (MDM) platforms (such as Microsoft Intune, VMware Workspace ONE, or Jamf) is a critical component for providing visibility into mobile assets that do not connect directly to the managed infrastructure via standard wired or wireless protocols.
According to theFortiNAC-F MDM Integration Guide, the communication between the FortiNAC-F appliance and the MDM server is handled throughREST APIcalls. FortiNAC-F acts as an API client, periodically polling the MDM server to retrieve device metadata, compliance status, and ownership information. If communication is failing, it is most likely because the API credentials (Client ID/Secret) are incorrect, the MDM's API endpoint is unreachable from the FortiNAC-F service port, or the SSL certificate presented by the MDM is not trusted by the FortiNAC-F root store.
While SSH (B) is used for switch CLI management and the Security Fabric (A) uses proprietary protocols for FortiGate synchronization, neither is the primary vehicle for MDM data exchange. SOAP API (D) is an older protocol that has been largely replaced by REST in modern FortiNAC integrations.
"FortiNAC integrates with MDM systems by utilizingREST APIcommunication to query the MDM database for device information. To establish this link, administrators must configure the MDM Service Connector with the appropriateAPI URLand authentication credentials. If the 'Test Connection' fails, verify that the FortiNAC can reach the MDM provider via theREST APIport (usually HTTPS 443)." —FortiNAC-F Administration Guide: MDM Integration and Troubleshooting.
An administrator manages a corporate environment where all users log into the corporate domain each time they connect to the network. The administrator wants to leverage login scripts to use a FortiNAC-F agent to enhance endpoint visibility
Which agent can be deployed as part of a login script?
Options:
Persistent
Dissolvable
Mobile
Passive
In a corporate domain environment where "enhanced endpoint visibility" is required, thePersistent Agentis the recommended choice. Unlike the Dissolvable Agent, which is temporary and intended for one-time compliance scans during registration, the Persistent Agent is an "install-and-stay-resident" application.
The Persistent Agent is specifically designed to be distributed through automated enterprise methods, includinglogin scripts, Group Policy Objects (GPO), or third-party software management tools. When deployed via a login script, the agent can be configured to silently install and immediately begin communicating with the FortiNAC-F service interface. Once active, it provides continuous visibility by reporting host details such as logged-on users, installed applications, and adapter information. It also listens for Windows session events (logon/logoff) to trigger automatic single-sign-on (SSO) registration in FortiNAC-F, ensuring that as soon as a user connects to the domain, their device is identified and assigned the correct network access policy.
"The Persistent Agent can be distributed to Windows domain machines vialogin scriptor by any other software distribution method your organization might use. The Persistent Agent remains installed on the host at all times. Once the agent is installed it runs in the background and communicates with FortiNAC at intervals established by the FortiNAC administrator." —FortiNAC-F Administration Guide: Persistent Agent Overview.
How can an administrator configure FortiNAC-F to normalize incoming syslog event levels across vendors?
Options:
Configure severity mappings.
Configure the vendor OUI settings.
Configure the security rule settings.
Configure event to alarm mappings.
FortiNAC-F serves as a central manager for security events originating from a diverse ecosystem of third-party security appliances, such as FortiGate, Check Point, and Cisco. Each vendor utilizes its own internal scale forseverity levelswithin syslog messages (e.g., Check Point uses a 1–5 scale, while others may use 0–7). To provide a consistent response regardless of the source, FortiNAC-F usesSeverity Mappingsto normalize these incoming values.
According to theFortiNAC-F Administration Guide, severity mappings allow the administrator to translate vendor-specific threat levels into standardizedFortiNAC Security Levels(such as High, Medium, or Low Violation). When a syslog message arrives, the parser extracts the vendor's severity code, and the system immediately references theSecurity Event Severity Level Mappingstable to determine how that event should be categorized internally. This normalization is vital because it allows a singleSecurity Alarmto be configured to respond to any "High Violation" event, whether it was reported as a "Critical" by one vendor or a "Level 5" by another. Without these mappings, the administrator would have to create separate, redundant security rules for every vendor to account for their different naming conventions and numerical scales.
"Each vendor defines its own severity levels for syslog messages. The following table shows the equivalent FortiNAC security level... To normalize these events, configure theSeverity Level Mappingsfound in the device integration guides. This allows FortiNAC to generate a consistent security event that can then trigger an alarm regardless of the reporting vendor's specific terminology." —FortiNAC-F Administration Guide: Vendor Severity Levels and Syslog Management.
During an evaluation of state-based enforcement, an administrator discovers that ports that should not be under enforcement have been added to enforcement groups.
In which view would the administrator be able to identify who added the ports to the groups?
(Selected)
Options:
The Admin Auditing view
The Event Management view
The Port Changes view
The Security Events view
In FortiNAC-F, accountability and forensic tracking of configuration changes are managed through theAdmin Auditingfunctionality. When an administrator performs an action that modifies the system state—such as creating a policy, changing a device's status, or adding a switch port to anEnforcement Group—the system generates an audit record. This record is essential for troubleshooting scenarios where unauthorized or accidental configuration changes have occurred, leading to unintended network behavior.
TheAdmin Auditingview (found underLogs > Admin Auditing) provides a comprehensive log of the "Who, What, and When" for every administrative session. Each entry includes the username of the administrator, the source IP address from which they accessed the FortiNAC-F console, a precise timestamp, and a detailed description of the modification. In the scenario described, where ports have been incorrectly added to enforcement groups, the Admin Auditing view allows a supervisor to filter by the specific "Port" or "Group" object to identify exactly which administrator executed the command.
In contrast, theEvent Managementview (B) is designed to monitor system and network events, such as RADIUS authentications, host connections, and SNMP trap arrivals. While it tracks system activity, it does not typically log the manual configuration changes performed by admins. ThePort Changesview (C) tracks the operational history of a port (such as VLAN assignment changes and host movements) but does not attribute the administrative assignment of the port to a group. Finally, theSecurity Eventsview (D) is dedicated to alerts triggered by security rules and external threat feeds.
"Admin Auditing displays a record of all modifications made to the FortiNAC-F system by an administrator. This view includes the administrator's name, the date and time of the change, and a description of the action taken. It is the primary resource for determining which administrative user performed a specific configuration change, such as modifying port group memberships or altering policy settings." —FortiNAC-F Administration Guide: Logging and Auditing Section.
Where should you configure MAC notification traps on a supported switch?
Options:
Only on ports that generate linkup and linkdown traps
Only on ports defined as learned uplinks
On all ports on the switch
On all ports except uplink ports
In FortiNAC-F,MAC notification traps(also known as MAC Move or MAC Change traps) are essential for achieving real-time visibility of endpoint connections and disconnections. When a device connects to a switch port, the switch generates an SNMP trap that informs FortiNAC-F of the new MAC address on that specific interface. This allows FortiNAC-F to immediately initiate the profiling and policy evaluation process without waiting for the next scheduled L2 poll.
According to theFortiNAC-F Administration GuideandSwitch Integrationdocumentation, MAC notification traps should be configured onall ports except uplink ports. Uplink ports are the interfaces that connect one switch to another or to the core network. Because these ports see the MAC addresses of every device on the downstream switches, enabling MAC notification on uplinks would cause the switch to send a massive volume of redundant traps to FortiNAC-F every time any device anywhere in the downstream branch moves or reconnects. This can overwhelm the FortiNAC-F process queue and degrade system performance.
By only enabling these traps on "edge" or "access" ports—where individual endpoints like PCs, printers, and VoIP phones connect—FortiNAC-F receives precise data regarding exactly where a device is physically located. Uplinks should be identified in the FortiNAC-F inventory as "Uplink" or "Learned Uplink," which tells the system to ignore MAC data seen on those specific ports.
"To ensure accurate host tracking and optimal system performance, SNMP MAC notification traps must be enabled on all access (downlink) ports.Do not enable MAC notification traps on uplink ports, as this will result in excessive and unnecessary trap processing. Uplink ports should be excluded to prevent the system from attempting to map multiple downstream MAC addresses to a single infrastructure interface." —FortiNAC-F Administration Guide: SNMP Configuration for Network Devices.
Refer to the exhibit.
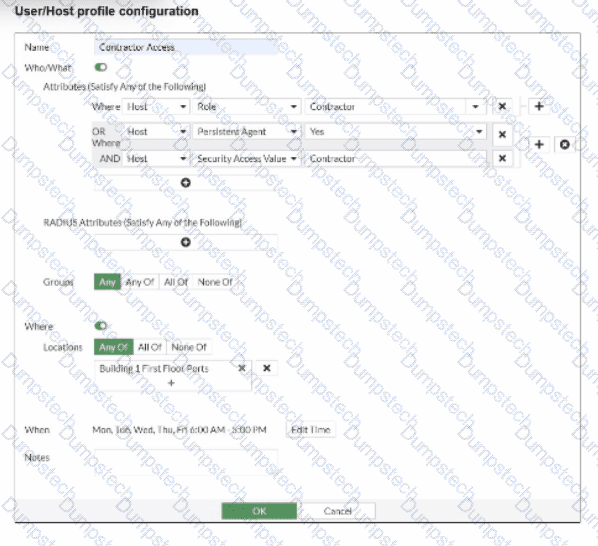
If a host is connected to a port in the Building 1 First Floor Ports group, what must also be true to match this user/host profile?
Options:
The host must have a role value of contractor, an installed persistent agent or a security access value of contractor, and be connected between 6 AM and 5 PM.
The host must have a role value of contractor or an installed persistent agent, a security access value of contractor, and be connected between 9 AM and 5 PM.
The host must have a role value of contractor or an installed persistent agent or a security access value of contractor, and be connected between 6 AM and 5 PM.
The host must have a role value of contractor or an installed persistent agent and a security access value of contractor, and be connected between 6 AM and 5 PM.
TheUser/Host Profilein FortiNAC-F is the fundamental logic engine used to categorize endpoints for policy assignment. As seen in the exhibit, the configuration uses a combination of Boolean logic operators (ORandAND) to define the "Who/What" attributes.
According to theFortiNAC-F Administrator Guide, attributes grouped together within the same bracket or connected by anORoperator require only one of those conditions to be met. In the exhibit, the first two attributes are "Host Role = Contractor"OR"Host Persistent Agent = Yes". This forms a single logical block. This block is then joined to the third attribute ("Host Security Access Value = Contractor") by anANDoperator. Consequently, a host must satisfyat least oneof the first two conditionsANDsatisfy the third condition to match the "Who/What" section.
Furthermore, the profile includesLocationandWhen(time) constraints. The exhibit shows the location is restricted to the "Building 1 First Floor Ports" group. The "When" schedule is explicitly set toMon-Fri 6:00 AM - 5:00 PM. For a profile to match,allenabled sections (Who/What, Locations, and When) must be satisfied simultaneously. Therefore, the host must meet the conditional contractor/agent criteria, possess the specific security access value, and connect during the defined 6 AM to 5 PM window.
"User/Host Profiles use a combination of attributes to identify a match. Attributes joined byORrequire any one to be true, while attributes joined byANDmust all be true. If aSchedule(When) is applied, the host must also connect within the specified timeframe for the profile to be considered a match. All criteria in the Who/What, Where, and When sections are cumulative." —FortiNAC-F Administration Guide: User/Host Profile Configuration.
Which two requirements must be met to set up an N+1 HA cluster? (Choose two.)
Options:
A FortiNAC-F manager
A FortiNAC-F device designated as a secondary
A dedicated VLAN for primary and secondary synchronization
At least two FortiNAC-F devices designated as primary
TheN+1 High Availability (HA)architecture was introduced in FortiNAC-F version 7.6 to provide a more scalable and flexible redundancy model compared to the traditional 1+1 active/passive setup. In an N+1 configuration, a single secondary (standby) appliance can provide coverage for multiple primary (active) Control and Application (CA) appliances.
To set up an N+1 HA cluster, there are two fundamental structural requirements:
A FortiNAC-F Manager (FortiNAC-M):Unlike standard 1+1 HA, which can be configured directly between two CAs, N+1 management is centralized. The FortiNAC-M acts as the orchestrator that manages the failover groups, monitors the health of the primaries, and coordinates the promotion of the secondary server if a primary fails.
A FortiNAC-F device designated as a Secondary:The cluster must have one appliance explicitly configured with theSecondary failover role. This device remains in a standby state, receiving database replications from all N primaries in its group until it is called upon to take over the functions of a failed unit.
While a cluster can support multiple primaries (D), it does not strictly require "at least two" to function as an N+1 group; it simply requires N primaries (where N ≥ 1). Additionally, N+1 is typically a Layer 3 managed solution via the Manager, meaning it does not mandate a "dedicated VLAN" for synchronization like some Layer 2 HA deployments.
"In FortiNAC-F 7.6,FortiNAC-Mfunctions as a manager to manage the N+1 Failover Groups... enabling N+M high availability for CAs. To create an N+1 Failover group, you should add thesecondary CAto the FortiNAC-M first, then add the primary CAs. The secondary CA is designed to take over the functionality of any single failed primary component." —FortiNAC-F 7.6.0 N+1 Failover Reference Manual.
When creating a user or host profile, which three criteria can you apply? (Choose three.)
Options:
Host or user group memberships
Host or user attributes
Adapter current VLAN
An applied access policy
Location
TheUser/Host Profileis the primary mechanism in FortiNAC-F for identifying and categorizing endpoints to determine their level of network access. According to theFortiNAC-F Administration Guide, a profile is built using a combination of criteria that define "Who" is connecting, "What" device they are using, and "Where" they are located on the network.
The three main categories of criteria available in the configuration are:
Host or User Attributes (B):This includes specific details such as the host's operating system, the user's role (e.g., Employee, Contractor), or custom attributes assigned to the record.
Host or User Group Memberships (A):Profiles can be configured to match endpoints that are members of specific internal FortiNAC groups or synchronized directory groups (like LDAP or Active Directory groups). This allows for broad policy application based on organizational structure.
Location (E):The "Where" component allows administrators to restrict a profile match to specific physical or logical areas of the network, such as a particular switch, a group of ports, or a specific SSID.
Criteria like an "applied access policy" (D) are theoutcomeof a profile match rather than a criterion used to define the profile itself. Similarly, the "Adapter current VLAN" (C) is a dynamic state that changes based on enforcement and is not a standard static identifier used for profile matching.
"User/Host Profiles are used to identify the hosts and users to which a policy will apply. Profiles are created by selecting various criteria in theWho/What(Attributes and Groups) andWhere(Locations) sections. Attributes can include Host Role, User Role, and OS. Group memberships allow matching based on internal or directory-based groups. Location criteria allow for filtering based on the device or port where the host is connected." —FortiNAC-F Administration Guide: User/Host Profile Configuration.
How can an administrator configure FortiNAC-F to normalize incoming syslog event levels across vendors?
Options:
Configure severity mappings.
Configure the vendor OUI settings.
Configure the security rule settings.
Configure event to alarm mappings.
FortiNAC-F serves as a central manager for security events originating from a diverse ecosystem of third-party security appliances, such as FortiGate, Check Point, and Cisco. Each vendor utilizes its own internal scale forseverity levelswithin syslog messages (e.g., Check Point uses a 1–5 scale, while others may use 0–7). To provide a consistent response regardless of the source, FortiNAC-F usesSeverity Mappingsto normalize these incoming values.
According to theFortiNAC-F Administration Guide, severity mappings allow the administrator to translate vendor-specific threat levels into standardizedFortiNAC Security Levels(such as High, Medium, or Low Violation). When a syslog message arrives, the parser extracts the vendor ' s severity code, and the system immediately references theSecurity Event Severity Level Mappingstable to determine how that event should be categorized internally. This normalization is vital because it allows a singleSecurity Alarmto be configured to respond to any " High Violation " event, whether it was reported as a " Critical " by one vendor or a " Level 5 " by another. Without these mappings, the administrator would have to create separate, redundant security rules for every vendor to account for their different naming conventions and numerical scales.
" Each vendor defines its own severity levels for syslog messages. The following table shows the equivalent FortiNAC security level... To normalize these events, configure theSeverity Level Mappingsfound in the device integration guides. This allows FortiNAC to generate a consistent security event that can then trigger an alarm regardless of the reporting vendor ' s specific terminology. " —FortiNAC-F Administration Guide: Vendor Severity Levels and Syslog Management.
Modal title
