Black Friday VIP Hour Limited Time 75% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code = simple75

Pass the Cisco CCST 100-160 Questions and answers with Dumpstech

Exam 100-160 Premium Access

View all detail and faqs for the 100-160 exam

Practice at least 50% of the questions to maximize your chances of passing.
Viewing page 2 out of 2 pages
Viewing questions 11-20 out of questions
Questions # 11:

A restaurant installs a second wireless router that only employees can use.

Which statement describes how to securely configure the new router?

Options:

A.

Configure the new router to filter IP addresses.

B.

Configure the SSID with broadcast disabled.

C.

Configure a higher signal strength to allow coverage in the parking lot.

D.

Configure the SSID with the same SSID used by the customer router.

Questions # 12:

An administrator wants to ensure that any files downloaded from the internet are automatically scanned for malicious code before execution. Which security control should be implemented?

Options:

A.

Host-based firewall

B.

Anti-malware with real-time protection

C.

VPN client

D.

Patch management system

Questions # 13:

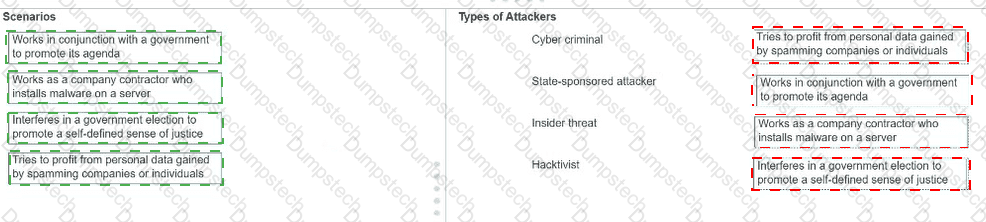
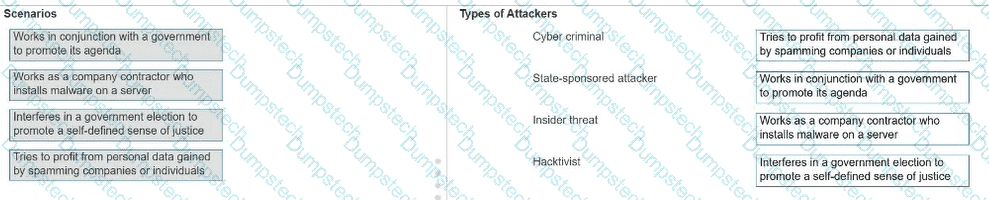
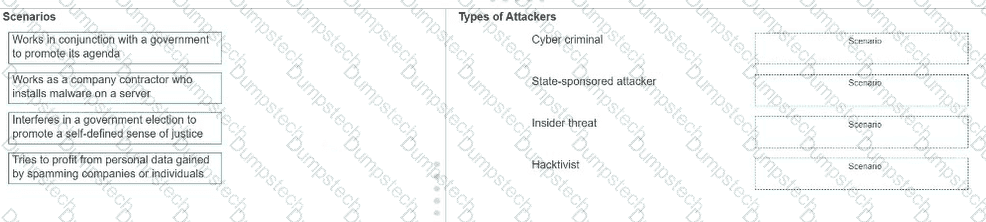
Move each scenario from the list on the left to the correct type of attacker on the right.

Note: You will receive partial credit for each correct answer.
Question # 13

Options:

Questions # 14:

Which security measure can prevent unauthorized devices from automatically connecting to a corporate network through unused switch ports?

Options:

A.

Port security

B.

VLAN trunking

C.

NAT

D.

VPN

Questions # 15:

You are going to perform a penetration test on a company LAN. As part of your preparation, you access the company’s websites, view webpage source code, and run internet searches to uncover domain information. You also use social media to gather details about the company and its employees.

Which type of reconnaissance activities are you performing?

Options:

A.

Passive

B.

Active

C.

Offline

D.

Invasive

Questions # 16:

Which two basic metrics should be taken into consideration when assigning a severity to a vulnerability during an assessment? (Choose 2.)

Options:

A.

The likelihood that an adversary can and will exploit the vulnerability

B.

The impacts that an exploit of the vulnerability will have on the organization

C.

The time involved in choosing replacement software to replace older systems

D.

The age of the hardware running the software that contains the vulnerability

Questions # 17:

A security administrator is implementing defense-in-depth.

Which set of solutions applies protection across different layers of the defense-in-depth approach?

Options:

A.

IPS/IDS, endpoint detection and response (EDR) solutions, strong passwords, and a firewall

B.

IPS/IDS, antivirus/anti-malware, a firewall, and endpoint detection and response (EDR) solutions

C.

Identity and access management (IAM), encryption, IPS/IDS, and endpoint detection and response (EDR) solutions

D.

Strong passwords, access controls, MFA, and identity and access management (IAM)

Questions # 18:

Your company is creating a BYOD policy to allow employees to join their personal smartphones to the company network.

Which three requirements are commonly included in a BYOD policy? (Choose 3.)

Options:

A.

Deletion of all personal data from the phone

B.

Synchronization of phone lock screen password with network access password

C.

Encryption of stored confidential corporate data

D.

Configuration of a strong password

E.

Upgrade of data plan to maximum available

F.

Installation of secure apps only

Questions # 19:

Several employees report that the company intranet website is no longer accepting their login credentials.

You attempt to access the site using its URL and notice several misspellings on the webpage. However, when you access the site directly using its IP address, it functions normally.

What should you do?

Options:

A.

Restore a backup copy of the authentication database.

B.

Verify the accuracy of the entry for the site in the local DNS server.

C.

Take the company web portal offline immediately.

D.

Update the web server software to the latest version.

Questions # 20:

Which wireless encryption technology requires AES to secure home wireless networks?

Options:

A.

WPA

B.

TKIP

C.

WPA2

D.

WEP

Viewing page 2 out of 2 pages
Viewing questions 11-20 out of questions