HP Certification Exams Pack
Everything from Basic, plus:
- Exam Name: HPE Network Security Expert Written Exam
- 75 Questions

Students Passed
Average Score
Questions came word for word
Years Teaching
Explore other related HP exams to broaden your certification path. These certifications complement your skills and open new opportunities for career growth.
Know how you can make it happen
If you're looking to secure Aruba Certified Switching Expert (HPE7-A10) certification, remember there's no royal path to it. It's your prep for this exam that can make the difference. Stay away from those low-quality exam PDFs and unreliable dumps that have no credibility. What you need is a simulated practice exam with practice questions that mirror the actual HPE7-A10 test environment.
To save you from frustration, Dumpstech comes with a comprehensive prep system that is clear, effective, and built to help you succeed without the least chance of failure. Whether you're looking for sample test questions or full exam practice questions for the HPE Network Security Expert Written Exam, our system delivers.
It's overwhelmingly recommended by thousands of Dumpstech's loyal customers as practical, relevant and intuitively crafted to match the candidates' actual exam needs. Our prep questions are designed to build real confidence for the SY0-701 test.
Dumpstech's HP exam HPE7-A10 questions are designed to deliver you the essence of the entire syllabus. Each question mirrors the real exam format and comes with an accurate and verified answer. These exam questions and answers give you the clarity you need. Dumpstech's prep system is not mere cramming; it is crafted to add real information and impart deep conceptual understanding to the exam candidates. After each test, review the practice exam answers to identify your weak spots.
Dumpstech's smart testing engine generates multiple mock tests to develop familiarity with the real exam format and learn thoroughly the most significant from the perspective of HP HPE7-A10 real exam. They also support you to revise the syllabus and enhance your efficiency to answer all exam practice questions within the time limit.
Dumpstech offers you the most authentic, accurate, and current information that liberates you from the hassle of searching for any other study resource. If you're looking for a free practice test with answers to evaluate our quality before you commit, download our free demo and see for yourself. This comprehensive resource equips you perfectly to develop confidence and clarity to answer exam queries.
Dumpstech's authentic and up-to-date content guarantees you success in the HPE Network Security Expert Written Exam certification exam. If you perchance you lose your exam despite your reliance on Dumpstech's exam questions PDF, Dumpstech doesn't leave you alone. You have the option of taking back refund of your money or try a different exam paying no additional amount.
If you want to crack the HPE Network Security Expert Written Exam (HPE7-A10) exam in one go, your journey starts here. Dumpstech is your real ally that gets you certified fast with the least possibility of losing your chance.
A customer needs the following rights for clients in the medical-mobile AOS firewall role on HPE Aruba Networking Mobility Controllers (MCs):
* They may receive IP addresses through DHCP.
* They may access DNS services at 10.8.9.7, and no other server.
* They may access all subnets in the 10.1.0.0/16 range, except 10.1.12.0/22, which must be denied.
* They must be denied access to other 10.0.0.0/8 subnets.
* They may access the Internet.
* They must be denied WLAN access for a period of time if they send any SSH traffic.
* They must be denied WLAN access for a period of time if they send any Telnet traffic.
* They must be denied access to all high-risk websites.
* External devices must not be allowed to initiate sessions with medical-mobile clients; they may send only return traffic.
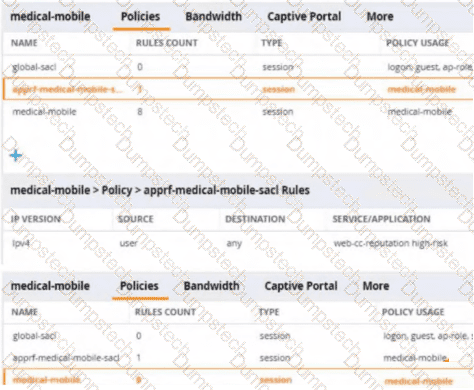
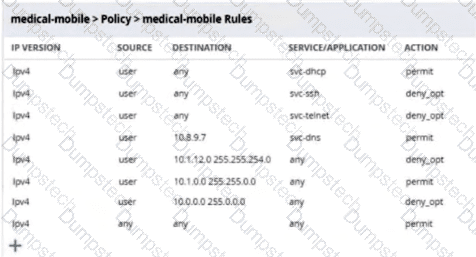
Refer to the scenario. The exhibits below show the role configuration.
* Role policies: `apprf-medical-mobile-sacl` (Rule: `user any web-cc-reputation high-risk deny`) and `medical-mobile` (8 rules configured).
Which setting not shown in the exhibits must you check to ensure the scenario requirements are met?
|
A
|
|---|
|
Explanation
The policy requirements dictate that clients assigned to the `medical-mobile` user role must be denied access to high-risk websites. In ArubaOS, filtering web traffic based on reputation categorization is powered by Web Content Classification (WebCC), which operates as a specialized component of Application Programming and Recognition Framework (AppRF). While the session ACL `apprf-medical-mobile-sacl` includes an ACE matching `web-cc-reputation high-risk`, this rule remains inert unless Web Content Classification and AppRF are globally enabled on the Mobility Controller and enabled within the assigned role configuration. WebCC queries cloud-hosted reputation feeds to dynamically score URLs into risk tiers. Regarding other requirements: the Policy Enforcement Firewall (PEF) is inherently stateful and bidirectional by default, automatically allowing session return traffic while preventing externally initiated sessions without manual stateful activation. Therefore, verifying that AppRF and WebCC are actively operational is the critical requirement. [References: ArubaOS 8 / AOS-10 User Guide – Web Content Classification (WebCC) and AppRF Engine Deployment., , , ]
|
A customer has an AOS-10 architecture that includes HPE Aruba Networking APs. The customer recently enabled WIDS at the high level on the APs. Administrators see several "ad hoc using valid SSID" events.
What should you explain?
|
A
|
|---|
|
Explanation
The 802.11 standard defines two primary operational modes: Infrastructure mode (where clients associate exclusively with an Access Point) and Independent Basic Service Set (IBSS), commonly known as Ad-Hoc mode (where stations communicate directly peer-to-peer without an AP). The WIDS signature ad hoc using valid SSID triggers when a device transmits 802.11 beacon frames configured in Ad-Hoc/IBSS mode while advertising the enterprise's authorized, valid SSID name. In enterprise security, this is a serious threat indicator: An attacker may be operating a software-defined Wi-Fi adapter broadcasting the corporate SSID in ad-hoc mode to trick adjacent client devices into establishing peer-to-peer associations, allowing the attacker to bypass access-layer firewalls and compromise connected endpoints directly. Alternatively, an attacker may be staging a Man-in-the-Middle (MitM) credential harvesting campaign or a Denial-of-Service (DoS) condition by poisoning the BSSID/channel mapping of legitimate corporate endpoints. This event represents deliberate wireless framing manipulation rather than a routine client driver glitch or GPO misconfiguration. Security teams should treat this detection as an active threat, immediately triangulating the transmitting MAC address and RF location using Central/RAPIDS to locate and contain the source. [References: ArubaOS 10 Security Architecture Guide – WIDS Detection Signatures, Ad-Hoc Networks, and Rogue Containment., , , ]
|
A hospital has an AOS-10 architecture managed by HPE Aruba Networking Central. The customer has deployed a pair of HPE Aruba Networking 9000 Series gateways with Security licenses at each clinic. The gateways implement IDS/IPS in IDS mode.
The Security Dashboard shows several recent events with the same signature, as shown below:
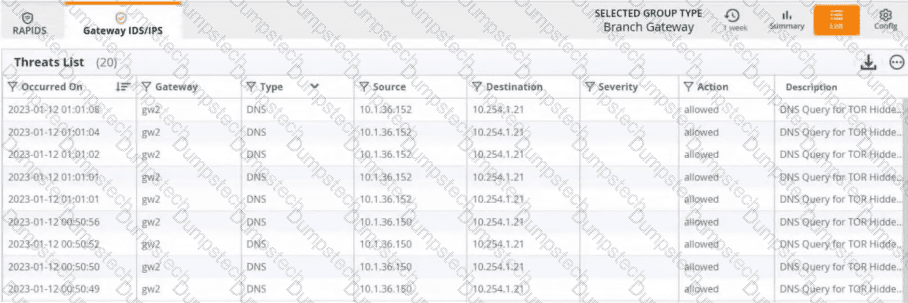
Occurred On: 2023-01-12 | Gateway: gw2 | Type: DNS | Source: 10.1.36.152 | Destination: 10.254.1.21 | Action: allowed | Description: DNS Query for TOR Hidden...
Refer to the scenario.
You have learned that nurse call stations are the source of the events. What can you conclude?
|
A
|
|---|
|
Explanation
The Onion Router (Tor) hidden service architecture utilizes randomized pseudo-top-level `.onion` domains to establish anonymized, encrypted communication channels. In enterprise healthcare networks, dedicated clinical IoT equipment—such as nurse call stations—operates with deterministic, proprietary communication profiles (e.g., local SIP, MQTT, or HTTP/HTTPS to local healthcare application servers). Nurse call systems have zero operational requirement to resolve or communicate with Tor hidden services. When an intrusion detection system (IDS) triggers alerts for Tor DNS queries originating from these specialized endpoints, it represents high-confidence anomalous behavior. Advanced malware, ransomware staging engines, and command-and-control (C2) frameworks frequently leverage Tor infrastructure to obfuscate outbound communication, exfiltrate data, or bypass perimeter firewalls. Because IDS mode only detects and logs threats without blocking them (as evidenced by `Action: allowed` in the dashboard), these endpoints remain active and potentially compromised. The security and networking teams must immediately quarantine and forensically investigate these stations. [References: HPE Aruba Networking Central – Threat Intelligence and Signature Analysis, Healthcare IoT Security Best Practices., , , ]
|
See how DumpsTech helps candidates pass with confidence.
Stay ahead in your career with the latest certification exams from leading vendors. DumpsTech brings you newly released exams with reliable study resources to help you prepare confidently.
Find answers to the most common questions about the HP HPE7-A10 exam, including what it is, how to prepare, and how it can boost your career.