75only - Ends in 0d 00h 00m 00s - Coupon code = 75only
Pass the Microsoft Certified: Information Security Administrator Associate SC-500 Questions and answers with Dumpstech
You have a Microsoft 365 tenant that uses Microsoft Security Copilot and Microsoft Defender XDR.
Access to Microsoft Defender XDR is managed by using Microsoft entra global roles.
The Phishing triage Agent is available in Microsoft Defender. The required agent prerequisites and approvals are complete
Two users will perform the following tasks:
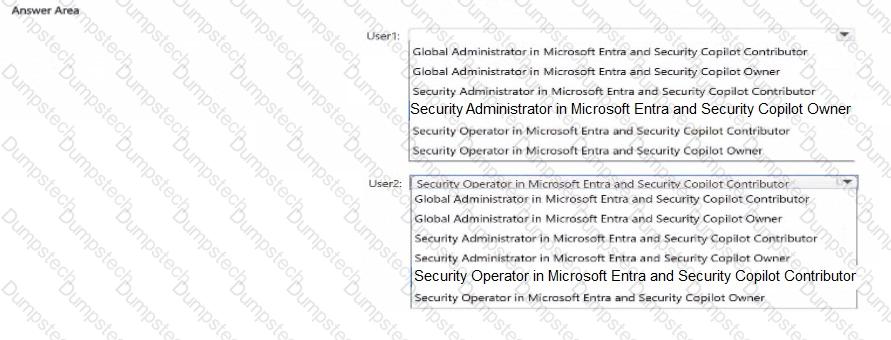
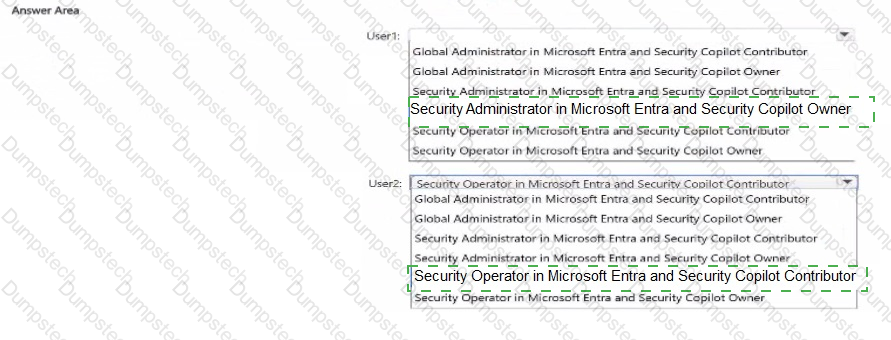
• User1 will enable and manage the Phishing Triage Agent settings.
• User2 will use Security Copilot in Microsoft Defender XDR to manage phishing incidents identified by the agent.
You need to assign the least-privileged built in Microsoft Entra role and Security Copilot role combination to each us Which roles should you assign to each user? To answer, select the appropriate options in the answer area.
You have an Azure management group named MG1 that contains two subscriptions named Sub1 and Sub? Both subscriptions are linked to a Microsoft Entra tenant that contains a security group named Group!
You need to ensure that the members of Group1 can assign roles to the resources in Sub1 and Sub2. The solution must follow the principle of least privilege.
Which role should you assign to Group1?
You have a Microsoft Entra tenant that uses Privileged Identity Management (PIM).
You need to modify the AI Administrator role settings to meet the following requirements:
•Elevated access must be evaluated by another administrator before it is granted
•Privileged access must be removed automatically after a fixed period.
Which two settings should you configure? Each correct answer presents part of the solution.
NOTE: Each correct selection is worth one point.
You have an Azure subscription named Sub1 that contains multiple virtual machines and an Azure key vault named KV1.
Each virtual machine has a system-assigned managed identity. Sub1 has Microsoft Defender for Servers enabled. Defender for Servers has agentless scanning enabled.
Some virtual machines use managed disks that are encrypted by using customer-managed keys stored in KV1.
You discover that the affected virtual machines fail to return agentless scanning results in Microsoft Defender for Cloud.
You need to ensure that agentless scanning can analyze the virtual machines.
What should you do?
You have an Azure subscription that contains the resources shown in the following table.
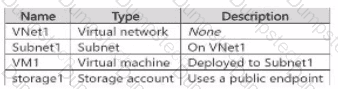
VM1 contains an application that accesses storage1. Another application accesses storage1 from a public IP address of 131.107.10.20.
For storage1, you set Public network access to Enabled from selected virtual networks and IP addresses. You add an IP network rule for 131.107.10.20.
After the configuration, only connections from 131.107.10.20 succeed.
You need to ensure that both VM1 and 131.107.10.20 can access storage1 over the public endpoint, while preventing all other access.
What should you do?
You have an Azure subscription named Sub1 that contains a storage account named storage1. Sub1 has Microsoft Defender for Storage enabled. Defender for Storage has malware scanning enabled.
You need to configure a solution that automates the remediation of malware detected in storage1.
What should you include in the solution?
You have a Microsoft Entra tenant that contains a user named Admin1 and is linked to an Azure subscription named Sub1.
Admin1 reports that the Custom recommendation option is unavailable in Microsoft Defender for Cloud as shown in the following exhibit.
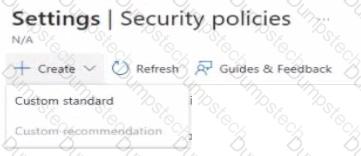
You need to ensure that Admin1 can create a custom recommendation. The solution must follow the principle of least privilege. What should you do?
You have an Azure subscription that contains a resource group named RG1.
RG1 contains a Microsoft Security Copilot deployment that is integrated with a Microsoft Sentinel workspace named Workspace1.
Analysts use the Security Copilot standalone experience to retrieve incidents by using the Microsoft Sentinel plugin.
A user named User1 can sign in to Security Copilot but cannot retrieve incidents from Workspace1. You verify that User1 lias only the Security Copilot Contributor role.
You need to ensure that User1 can retrieve the incidents. The solution must follow the principle of least privilege and NOT require any configuration changes to Security Copilot.
Which role should you assign to User1?
You are implementing security controls for an Azure Storage account by using infrastructure as code (IaC).
You deploy the following Bicep code.
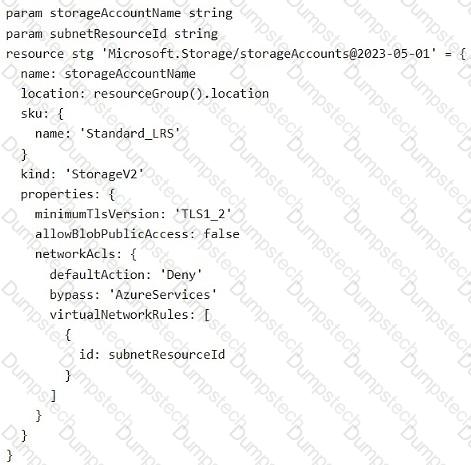
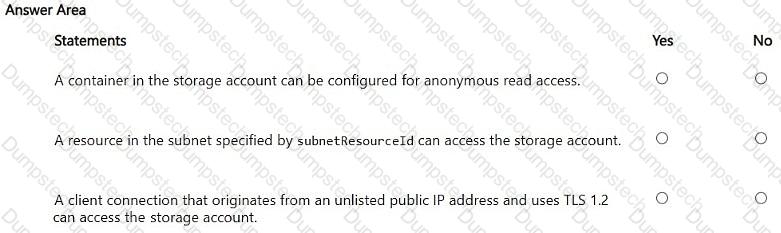
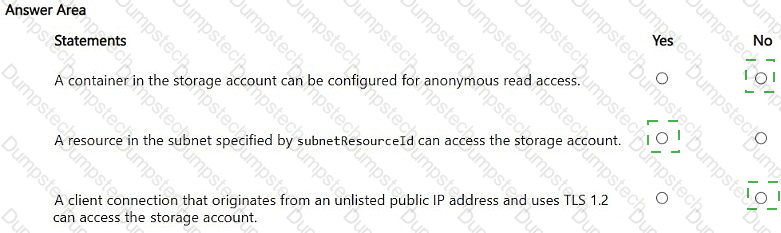
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
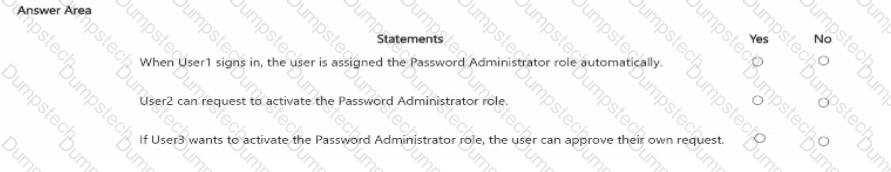
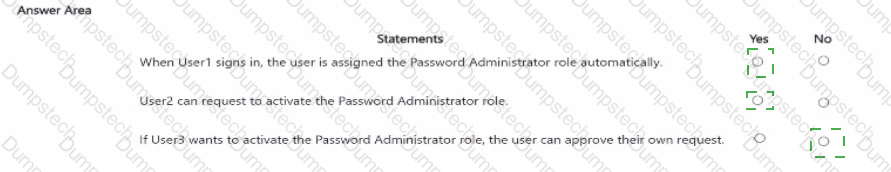
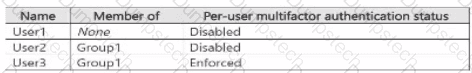
You have a Microsoft Entra tenant named contoso.com that contains the users shown in the following table.
Microsoft Entra Privileged Identity Management (PIM) is used in contoso.com.
In PIM, the Password Administrator role has the following settings: