
75only - Ends in 0d 00h 00m 00s - Coupon code = 75only
Pass the Microsoft Certified: Information Security Administrator Associate SC-500 Questions and answers with Dumpstech
You have a Microsoft Sentinel workspace named Workspace1.
You hire a security consultant. You provide the consultant with a guest account named User1 in your Microsoft Entra tenant
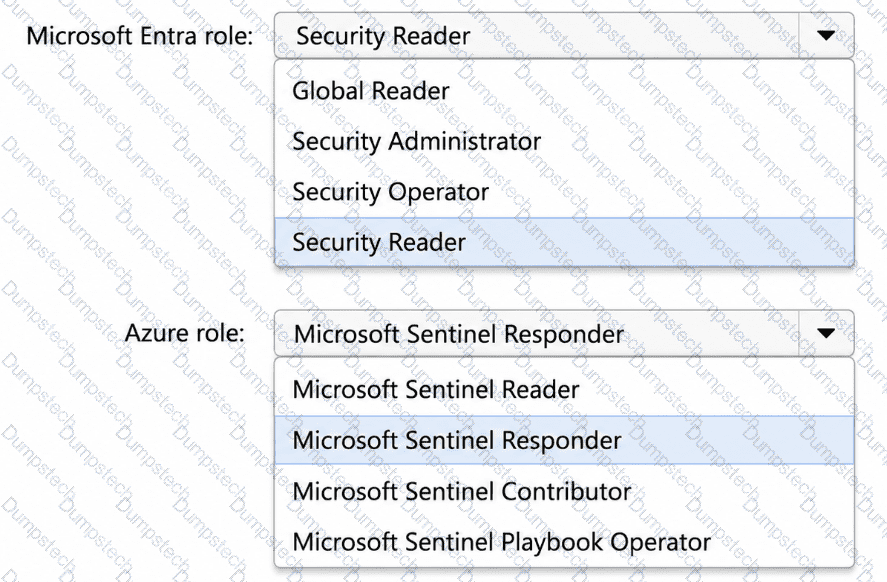
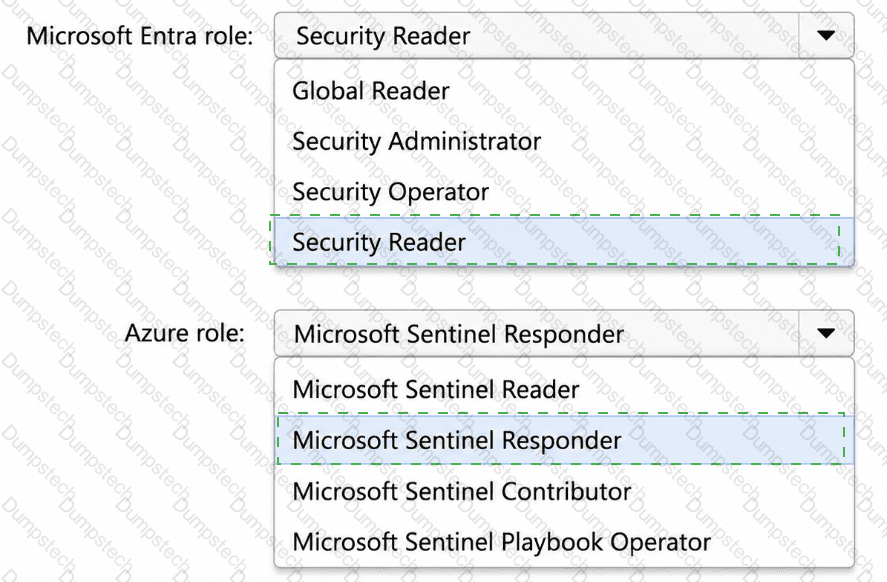
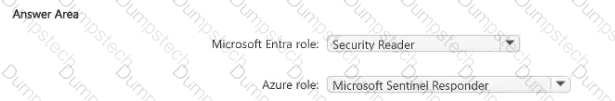
You need to enable User1 to assign incidents in Workspace1.
Which roles should you assign to User1? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
You have three internet-facing Azure App Service web apps named App1, App2, and App1 Each app uses built-in authentication.
App2 hosts a backend API.
Some corporate users can sign in to App2, even though they should NOT be able to use the API.
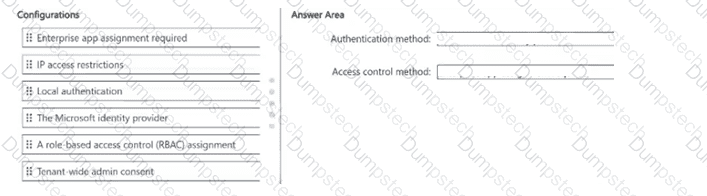
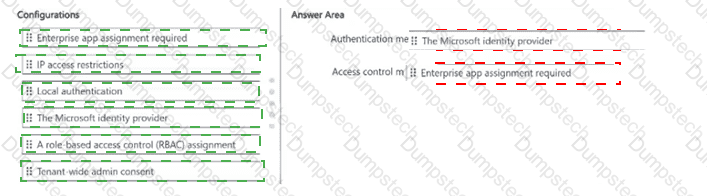
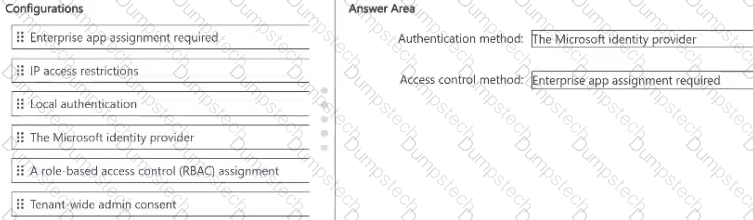
You need to restrict App2 access to assigned Microsoft Entra users and groups.
What should you configure for App2? To answer, drag the appropriate configurations to the correct methods. Each configuration may be used once, more than once, or not at all. You may need to drag the split bar between panes or scroll to view content.
NOTE: Each correct selection is worth one point.
You have an Azure SQL Database logical server named Server1 that contains a database named DB1.
You need to configure authentication for Server1 to meet the following requirements;
•SQL authentication cannot be used for any databases on Server1.
•The solution must be enforced centrally at the server level.
What should you do?
You have Microsoft Security Copilot agents that authenticate by using Microsoft Entra service principals.
You receive a Microsoft Defender alert triggered by the anomalous OAuth authentication of an agent ' s Microsoft Entra service principal.
You need to assess the impact of the agent identity and identify which resources are affected if the identity is abused for lateral movement The solution must minimize administrative effort.
What should you do?
You have an Azure virtual network named VNet1 that contains three subnets named Subnet1, Subnet2 and Subnet3. A single network security group (NSG) named NSG1 is associated with all the subnets. You have the following virtual machines:
•VM1 on Subnet1
•VM2 on Subnet2
VM3 on Subnet3
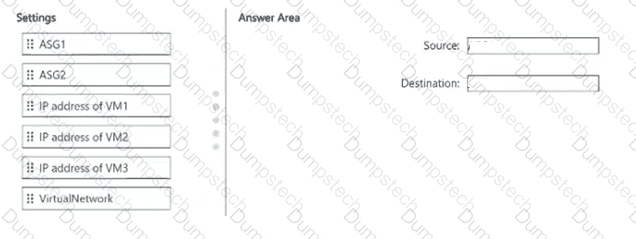
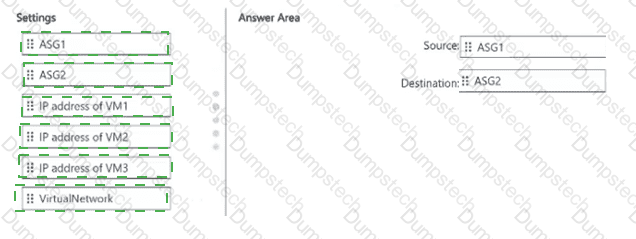
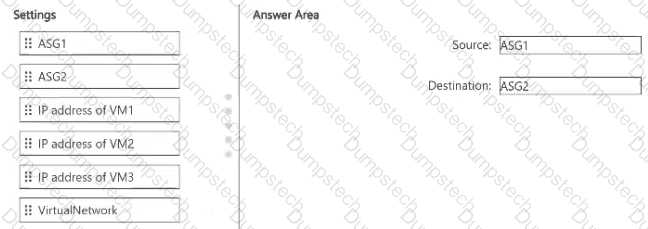
You create two application security groups named ASG1 and ASG2. VM2 is a member of ASG1, and VM3 is a member of ASG2.
You need to ensure that only VM2 can connect to VM3. The solution must continue to work if the private IP address of VM2 changes.
How should you configure the inbound rule on NSG1 ? To answer, drag the settings to the correct configurations. Each setting may be used once, more than once, or not at all. You may need to drag the split bar between panes or scroll to view content.
NOTE: Each correct selection is worth one point.
An application run2 on VM1 and VM2. The application is being migrated from storage account key authentication to Microsoft Entra authentication.
You review the current configuration and identify the following:
• VM1 and VM2 each have a system-assigned managed identity.
• Each application instance requests tokens by using only the local system-assigned managed identity.
• Network access to storage 1 from VMI and VM2 is allowed.
• No Azure RBAC data roles are assigned to the managed identities on storage1.
You need to enable the application on VM1 and VM2 to read and write blob data in storage1 by using Microsoft Entra authentication without changing how the application requests tokens.
Solution: You create a private endpoint for the blob service of storage1.
Does this meet the goal?
You have an Azure subscription named Sub1 that contains a storage account named storage1. Sub1 has Microsoft Defender for Storage enabled. Defender for Storage has malware scanning enabled.
You need to configure a solution that automates the remediation of malware detected in storage1.
What should you include in the solution?
You have an Azure subscription that has Microsoft Defender for Cloud enabled.
You have an Amazon Web Services (AWS) account connected to Defender for Cloud that has the Defender Cloud Security Posture Management (CSPM) plan enabled.
You need to identify the potential impact of security incidents that exploit multiple risks reported by Defender CSPM.
What should you use?
You have an Azure subscription that contains a resource group named RG1 and has Microsoft Defender for Cloud enabled.
You connect an Amazon Web Services (AWS) account to Defender for Cloud by creating the AWS connector in RG1.
You have a Microsoft Entra group named Group1 that contains the user accounts of the security analysts at your company.
You need to ensure that the members of Group1 can view multicloud recommendations and security alerts for the connected AWS account. The solution must follow the principle of least privilege.
Which role should you assign to Group1 for RG1?
You have a Microsoft Entra tenant that contains the users shown in the following table.
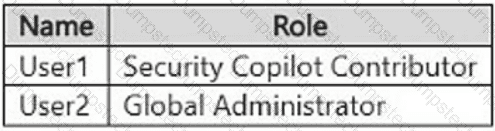
You have a Microsoft Security Copilot workspace.
From Microsoft Security Store, you plan to deploy a partner-built agent named Agent1 that requires access to Microsoft Intune.
When User1 selects Agent1, the Get agent option is unavailable.
You need to enable User1 to complete the agent setup. The solution must follow the principle of least privilege.
What should you do first?
