75only - Ends in 0d 00h 00m 00s - Coupon code = 75only
Pass the Splunk Cybersecurity Defense Analyst SPLK-5002 Questions and answers with Dumpstech
An engineer wants to track and report on all authentication to corporate assets and wants to prioritize critical assets without significantly increasing the number of findings created. What process could be used to accomplish this goal?
Which syntax is correct to create two new rows on an existing threat intelligence collection?
What is a key feature of effective security reports for stakeholders?
Which features are crucial for validating integrations in Splunk SOAR? (Choose three)
A detection engineer is using a threat defense informed strategy to define use cases. Which Splunk app would best facilitate their use case development process by cross referencing detections with the MITRE ATT & CK Framework?
An effective method for building automation workflows is to follow the OODA (Observe, Orient, Decide, Act) loop stages. When transitioning between the Decide and Act stages, what additional step should be included before automating the Act stage?
A Splunk administrator needs to integrate a third-party vulnerability management tool to automate remediation workflows. What is the most efficient first step?
For detections that leverage a CIM data model, which aspect of the configuration is responsible for determining which indexes are being searched?
The threat-hunting team has identified suspicious activity. An analyst manually creates a notable event using an event action to track the activity. How should a detection engineer ensure this activity automatically produces findings in the future?
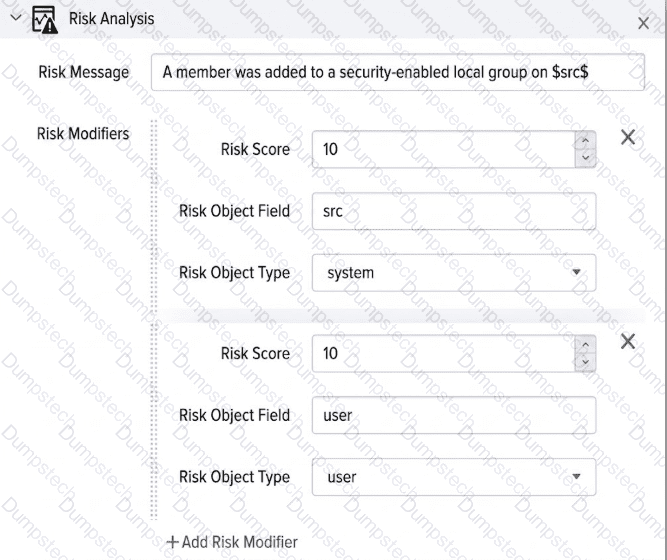
Based on this example image, if it is detected that a member has been added to a security-enabled local group, how many risk events will be created?