
75only - Ends in 0d 00h 00m 00s - Coupon code = 75only

Pass the Splunk Cybersecurity Defense Analyst SPLK-5002 Questions and answers with Dumpstech

Exam SPLK-5002 Premium Access

View all detail and faqs for the SPLK-5002 exam

Practice at least 50% of the questions to maximize your chances of passing.
Viewing page 2 out of 4 pages
Viewing questions 11-20 out of questions
Questions # 11:

Which practices strengthen the development of Standard Operating Procedures (SOPs)? (Choose three)

Options:

A.

Regular updates based on feedback

B.

Focusing solely on high-risk scenarios

C.

Collaborating with cross-functional teams

D.

Including detailed step-by-step instructions

E.

Excluding historical incident data

Questions # 12:

What document can be helpful in understanding the prioritization of risk when comparing entities in an organization?

Options:

A.

A hierarchical organization chart

B.

Infrastructure architecture diagrams

C.

Application architecture diagrams

D.

Business Continuity or Disaster Recovery plan

Questions # 13:

Which of the following actions will allow access to a list of alert actions via the API?

Options:

A.

| rest /services/alerts/adaptive_response_action

B.

| rest /services/alerts/correlationsearches

C.

| rest /services/alerts/alert actions/_acl

D.

| rest /services/alerts/alert_actions

Questions # 14:

One of the goals of a detection engineer is to facilitate the triage process by providing the analyst as much context as possible. One way of accomplishing this is to provide context options through the use of which of the following settings?

Options:

A.

Correlation Search Name

B.

Risk Object Name

C.

Risk Analysis Adaptive Response Action

D.

Drill-down search

Questions # 15:

In Enterprise Security, what is the name of the threat intelligence lookup pertaining to files?

Options:

A.

file_hash

B.

file_intel

C.

user_intel

D.

user_hash

Questions # 16:

A cyber defense engineer plays a role in maintaining a secure SOAR Cloud configuration. Which network security statement is correct about SOAR Cloud?

Options:

A.

Splunk Cloud initiates an outbound SSL connection to both the Automation Broker and managed endpoints.

B.

The Automation Broker initiates an outbound SSL connection to Splunk Cloud, and also initiates an outbound connection to the managed endpoints.

C.

The Automation Broker initiates an inbound SSL connection to Splunk Cloud, and also initiates an outbound connection to the managed endpoints.

D.

The Automation Broker initiates an outbound SSL connection to Splunk Cloud, and the managed endpoint initiates an outbound connection to the Automation Broker.

Questions # 17:

Which phase of the incident response lifecycle would cause the least amount of friction when replacing manual steps with automation?

Options:

A.

Rendering a verdict

B.

Triage

C.

Containment

D.

Remediation

Questions # 18:

What is the best method to operationalize the results of a threat hunt for daily use by SOC analysts?

Options:

A.

Create monthly reports based on the documented findings.

B.

Communicate findings based on the hunt.

C.

Communicate gaps to the architecture teams.

D.

Create detections based on the documented findings.

Questions # 19:

Based on the provided screenshot, it ' s discovered that different machines or accounts have been associated with the shown threat objects.
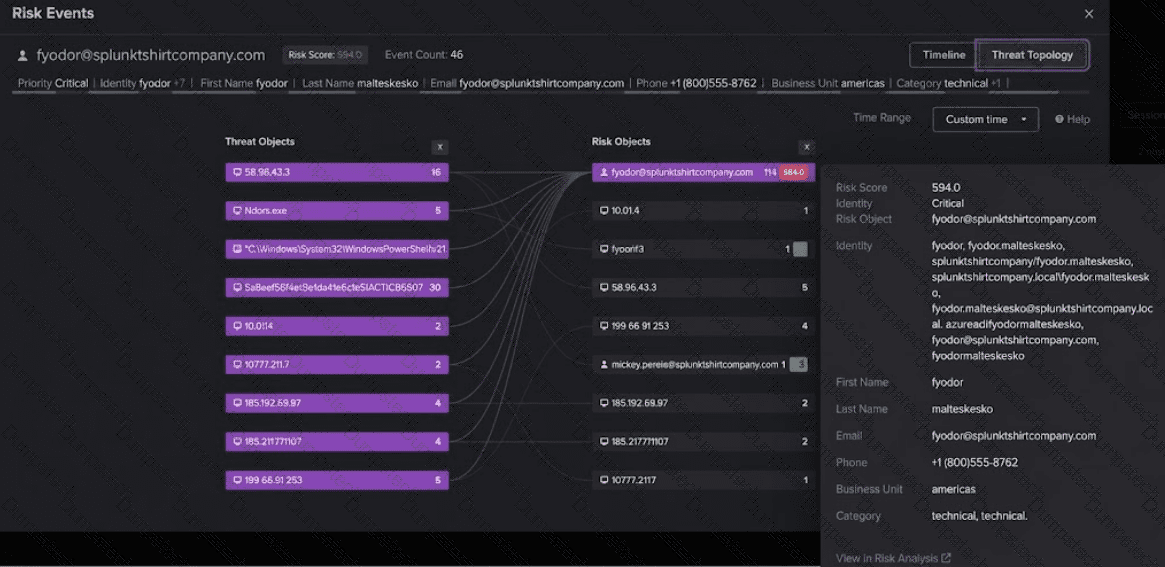
Question # 19

Enterprise Security has identified that these machines and accounts all point back to one owner - Fyodor. Which two frameworks in ES are responsible for programmatically associating this information together?

Options:

A.

Threat Intelligence, Assets & Identities

B.

Risk, Incident Review

C.

Risk, Assets & Identities

D.

Threat Intelligence, Risk

Questions # 20:

Which of the following macro values will exclude all of the company networks if it is called from the following search?

index=firewall sourcetype=pan\:traffic NOT " company_networks "

Options:

A.

(src_ip IN (151.157.30.0/24, 26.06.18.0/24))

B.

NOT (src_ip IN (151.157.30.0/24, 26.06.18.0/24))

C.

NOT (src_ip=151.157.30.0/24 AND src_ip=26.06.18.0/24)

D.

(src_ip=151.157.30.0/24 AND src_ip=26.06.18.0/24)

Viewing page 2 out of 4 pages
Viewing questions 11-20 out of questions