
75only - Ends in 0d 00h 00m 00s - Coupon code = 75only

Pass the Splunk Cybersecurity Defense Analyst SPLK-5002 Questions and answers with Dumpstech

Exam SPLK-5002 Premium Access

View all detail and faqs for the SPLK-5002 exam

Practice at least 50% of the questions to maximize your chances of passing.
Viewing page 1 out of 4 pages
Viewing questions 1-10 out of questions
Questions # 1:

An engineer wants to track and report on all authentication to corporate assets and wants to prioritize critical assets without significantly increasing the number of findings created. What process could be used to accomplish this goal?

Options:

A.

Decrease the risk score of non-critical assets in all existing detections.

B.

Add all access attempts to the Risk Index and increase criticality of critical assets.

C.

Add the critical assets to the risk data model.

D.

Determine a general risk rule for all access attempts to all assets, and then increase the Risk Factor for critical assets.

Questions # 2:

Which syntax is correct to create two new rows on an existing threat intelligence collection?

Options:

A.

curl -k -u admin\:pass https://localhost:8089/services/data/threat_intel/item/email_intel -d item= ' [{ " src_user " : " user_new " , " subject " : " click this " },{ " src_user " : " user2_new " , " subject " : " click this " }] ' -G -X

B.

curl -k -u admin\:pass https://localhost:8089/services/data/threat_intel/item/email_intel -d item= ' [{ " src_user " : " user_new " , " subject " : " click this " }] '

C.

curl -k -u admin\:pass https://localhost:8089/services/data/threat_intel/item/email_intel -d item= " [{ " src_user " : " user_new " , " subject " : " click this " },{ " src_user " : " user2_new " , " subject " : " click this " }] "

D.

curl -k -u admin\:pass https://localhost:8089/services/data/threat_intel/item/email_intel -d item= ' [{ " src_user " : " user_new " , " subject " : " click this " }] ' -G -X

Questions # 3:

What is a key feature of effective security reports for stakeholders?

Options:

A.

High-level summaries with actionable insights

B.

Detailed event logs for every incident

C.

Exclusively technical details for IT teams

D.

Excluding compliance-related metrics

Questions # 4:

Which features are crucial for validating integrations in Splunk SOAR? (Choose three)

Options:

A.

Testing API connectivity

B.

Monitoring data ingestion rates

C.

Verifying authentication methods

D.

Evaluating automated action performance

E.

Increasing indexer capacity

Questions # 5:

A detection engineer is using a threat defense informed strategy to define use cases. Which Splunk app would best facilitate their use case development process by cross referencing detections with the MITRE ATT & CK Framework?

Options:

A.

Supporting add-on for MITRE ATT & CK

B.

Splunk Security Essentials App

C.

Enterprise Security

D.

Enterprise Security Content Update App

Questions # 6:

An effective method for building automation workflows is to follow the OODA (Observe, Orient, Decide, Act) loop stages. When transitioning between the Decide and Act stages, what additional step should be included before automating the Act stage?

Options:

A.

Validate response data paths from the Decide stage.

B.

Validate if the asset, identity, or service has an exemption.

C.

Create a new automation playbook.

D.

Create a new response template.

Questions # 7:

A Splunk administrator needs to integrate a third-party vulnerability management tool to automate remediation workflows. What is the most efficient first step?

Options:

A.

Set up a manual alerting system for vulnerabilities

B.

Use REST APIs to integrate the third-party tool with Splunk SOAR

C.

Write a correlation search for each vulnerability type

D.

Configure custom dashboards to monitor vulnerabilities

Questions # 8:

For detections that leverage a CIM data model, which aspect of the configuration is responsible for determining which indexes are being searched?

Options:

A.

The data model ' s constraint macro.

B.

The data model ' s index list.

C.

The data model ' s root expression.

D.

The data model ' s dataset hierarchy.

Questions # 9:

The threat-hunting team has identified suspicious activity. An analyst manually creates a notable event using an event action to track the activity. How should a detection engineer ensure this activity automatically produces findings in the future?

Options:

A.

Create a SOAR playbook to identify events matching the activity and assign an urgency.

B.

Create a correlation search to produce notable events for the activity.

C.

Create a SOAR playbook to assign risk modifiers for events matching the activity.

D.

Create a risk modifier for events matching the activity.

Questions # 10:

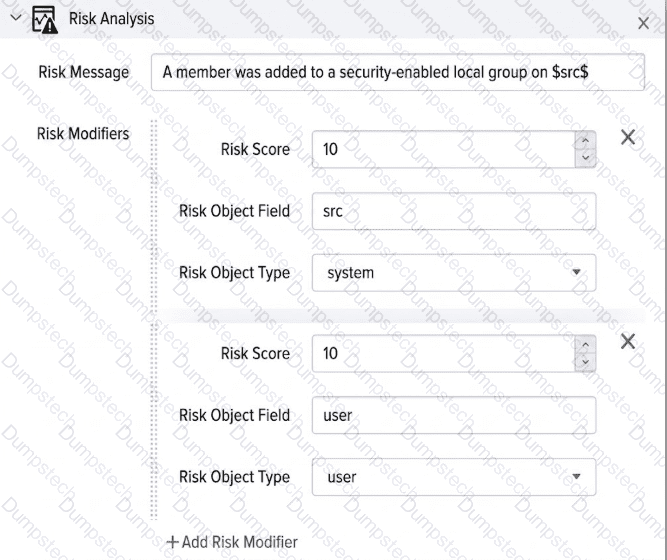
Based on this example image, if it is detected that a member has been added to a security-enabled local group, how many risk events will be created?
Question # 10

Options:

A.

20

B.

1

C.

10

D.

2

Viewing page 1 out of 4 pages
Viewing questions 1-10 out of questions