Winter Sale Limited Time 75% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code = simple75
Pass the Microsoft Certified: Information Security Administrator Associate SC-500 Questions and answers with Dumpstech
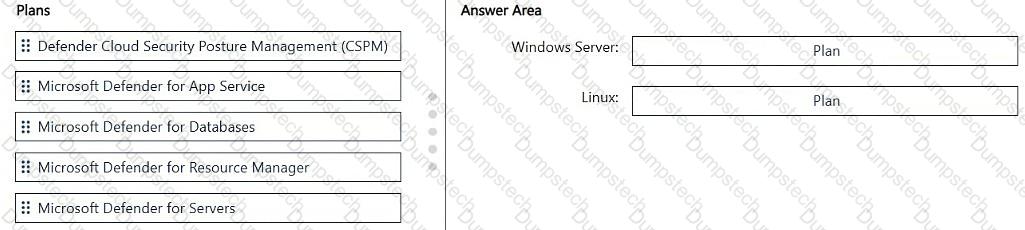
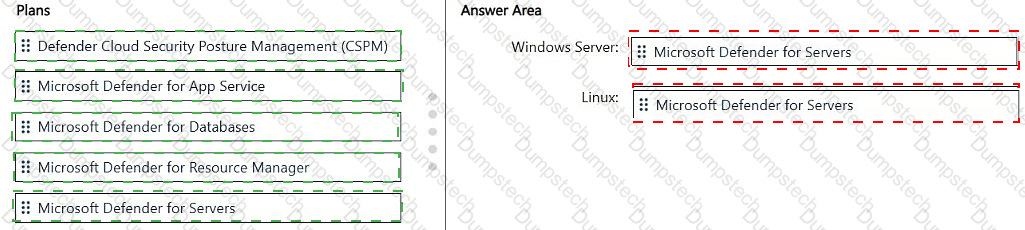
You have an Azure subscription named Sub1. Sub1 contains 60 virtual machines that run either Window Server or Linux.
All the Windows Server virtual machines host line-of-business (LOB) applications and all the Linux virtual machines host backend databases.
You need to enable malware protection for the virtual machines.
Which Microsoft Defender for Cloud plan should you enable for each type of virtual machine? To answer, drag the appropriate plans to the correct virtual machine types. Each plan may be used once, more than once, or not at all. You may need to drag the split bar between panes or scroll to view content.
NOTE: Each correct selection is worth one point.
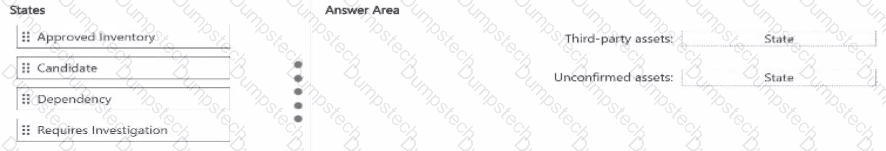
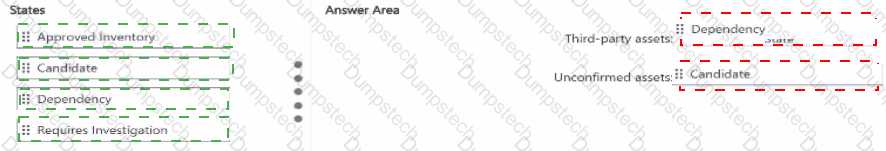
You have a Microsoft Defender External Attack Surface Management (Defender EASM) resource that discovers internet-facing assets for a company named Contoso, Ltd.
You need to classify the assets lo meet the following requirements.
• Third-party infrastructure assets must be tracked separately from assets owned by Contoso.
• Assets with unconfirmed ownership must remain outside the owned inventory until ownership is verified.
How should you classify the assets? To answer, drag the appropriate asset states to the correct assets. Each state may be used once, more than once or not at all. You may need to drag the split bar between panes or scroll to view content.
You have an Azure Subscription that contains the storage accounts shown in the following table.
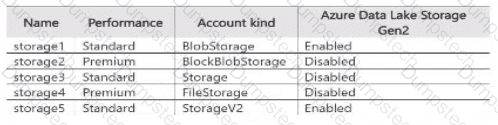
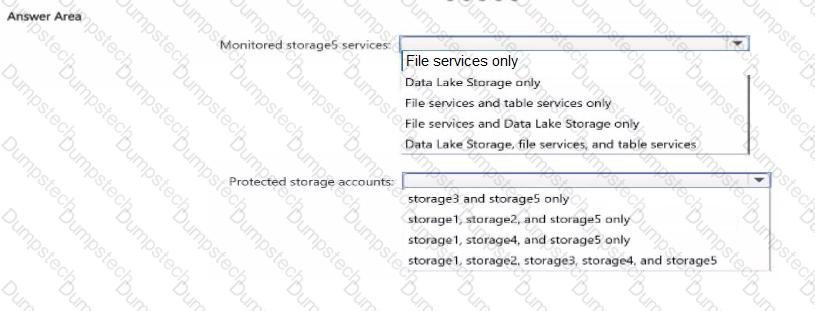
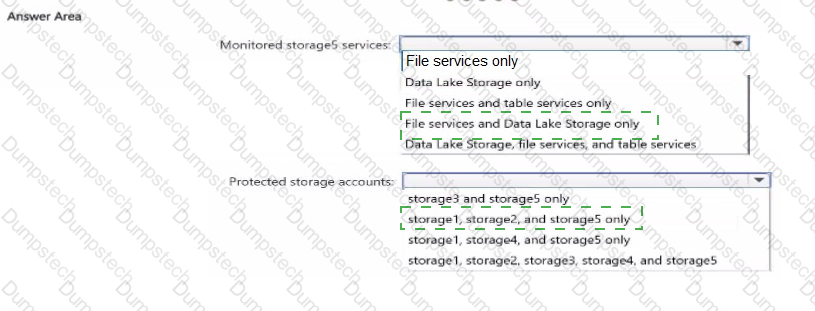
You enable Microsoft Defender for Storage.
Which storage services of storage5 are monitored by Microsoft for Storage which storage accounts are protected by.
You have an Azure subscription that uses Microsoft Defender for Cloud.
You have accounts for the following cloud services:
Alibaba Cloud
Amazon Web Services (AWS)
Google Cloud Platform (GCP)
What can you add to Defender for Cloud?
You have an Azure subscription that uses Microsoft Defender for Cloud.
You have an Amazon Web Services (AWS) account.
You need to ensure that when you deploy a new AWS Elastic Compute Cloud (EC2) instance, the Microsoft Defender for Servers agent installs automatically.
What should you configure first? sc new
You have an Azure subscription that contains a resource group named RG1 and has Microsoft Defender for Cloud enabled.
You connect an Amazon Web Services (AWS) account to Defender for Cloud by creating the AWS connector in RG1.
You have a Microsoft Entra group named Group1 that contains the user accounts of the security analysts at your company.
You need to ensure that the members of Group1 can view multicloud recommendations and security alerts for the connected AWS account. The solution must follow the principle of least privilege.
Which role should you assign to Group1 for RG1?
You have an Azure subscription that contains an Azure SQL Database logical server named SQL1 and an Azure virtual machine named VM1. VM1 uses a private IP address only. The Firewall and virtual networks settings for SQL1 are shown in the following exhibit.
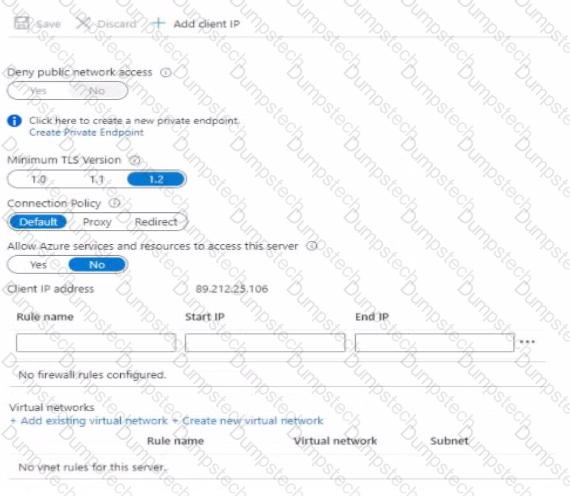
You need to ensure that VM1 can connect to SQL1. The solution must use the principle of least privilege.
What should you do on the SQL1 Firewall and virtual network settings?
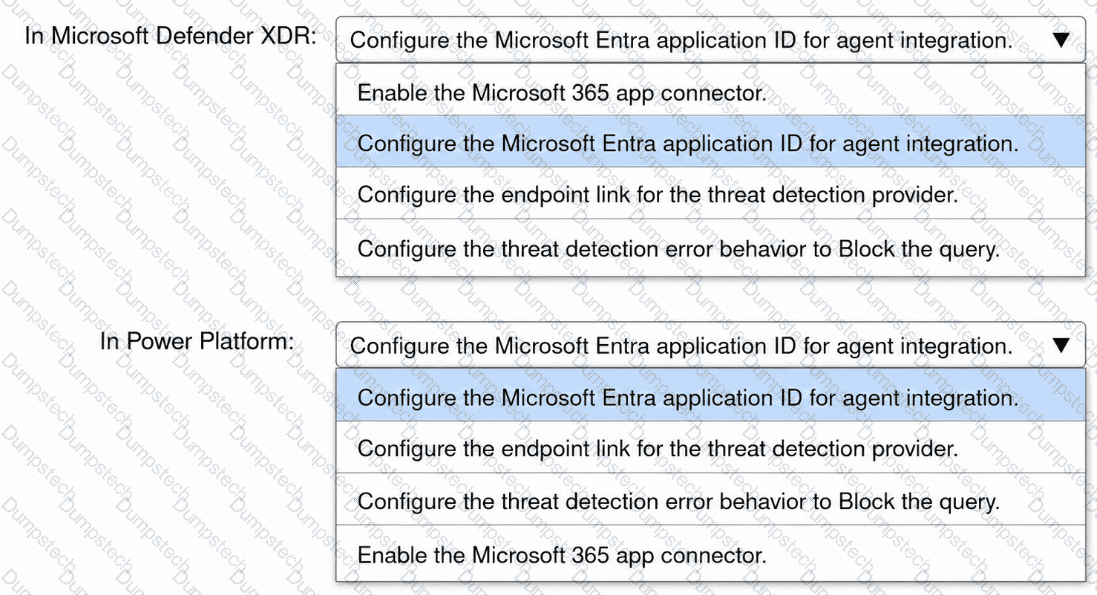
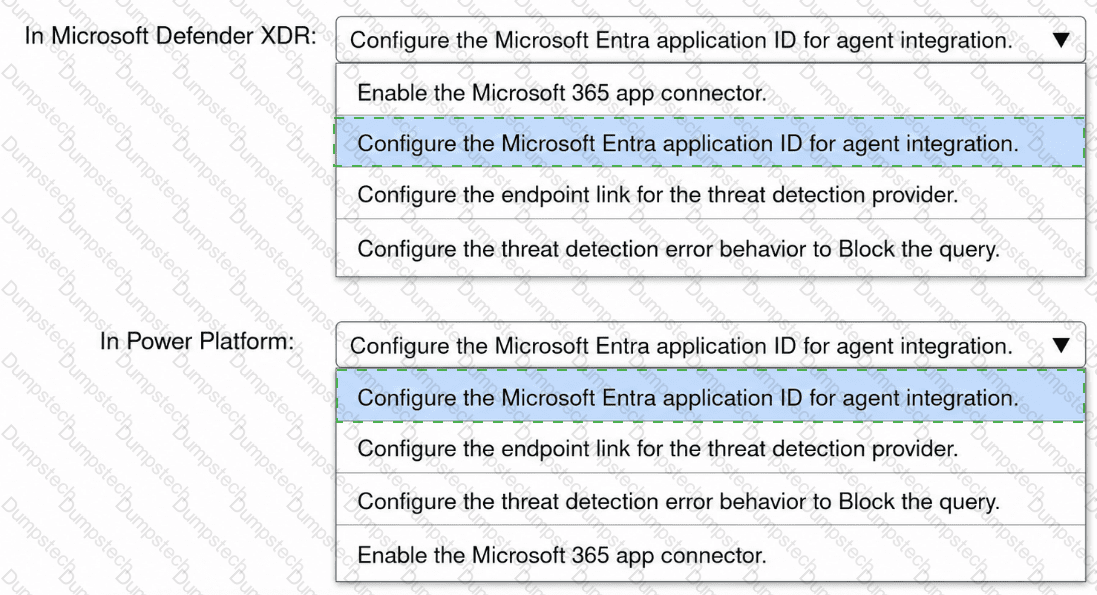
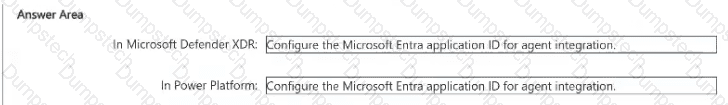
You have a Microsoft Defender XDR environment.
You have a Microsoft Power Platform environment where makers publish custom Microsoft Copilot Studio agents.
You need to enable real-time protection so that suspicious tool invocations are blocked before an agent runs actions, and related alerts appear in the Microsoft Defender portal.
What should you do? To answer, drag the appropriate actions to the correct services. Each action may be used once, more than once, or not at all. You may need to drag the split bar between panes or scroll to view content.
NOTE: Each correct selection is worth one point.
You have an Azure subscription named Sub1 that contains a storage account named storage1. Sub1 has Microsoft Defender for Storage enabled. Defender for Storage has malware scanning enabled.
You need to configure a solution that automates the remediation of malware detected in storage1.
What should you include in the solution?
You have an Azure Subscription that contains the Azure App Service web apps shown in the following table.
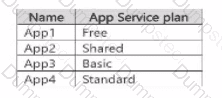
You purchase custom SSL certificates from a trusted third-party authority. To which apps can you assign the custom SSL certificates?
