75only - Ends in 0d 00h 00m 00s - Coupon code = 75only

Pass the Cisco CCNP Security 350-701 Questions and answers with Dumpstech

Exam 350-701 Premium Access

View all detail and faqs for the 350-701 exam

Practice at least 50% of the questions to maximize your chances of passing.
Viewing page 11 out of 16 pages
Viewing questions 151-165 out of questions
Questions # 151:

A network engineer is tasked with configuring a Cisco ISE server to implement external authentication against Active Directory. What must be considered about the authentication requirements? (Choose two.)

Options:

A.

RADIUS communication must be permitted between the ISE server and the domain controller.

B.

The ISE account must be a domain administrator in Active Directory to perform JOIN operations.

C.

Active Directory only supports user authentication by using MSCHAPv2.

D.

LDAP communication must be permitted between the ISE server and the domain controller.

E.

Active Directory supports user and machine authentication by using MSCHAPv2.

Questions # 152:

When using Cisco AMP for Networks which feature copies a file to the Cisco AMP cloud for analysis?

Options:

A.

Spero analysis

B.

dynamic analysis

C.

sandbox analysis

D.

malware analysis

Questions # 153:

What are two Detection and Analytics Engines of Cognitive Threat Analytics? (Choose two)

Options:

A.

data exfiltration

B.

command and control communication

C.

intelligent proxy

D.

snort

E.

URL categorization

Questions # 154:

Which ID store requires that a shadow user be created on Cisco ISE for the admin login to work?

Options:

A.

RSA SecureID

B.

Internal Database

C.

Active Directory

D.

LDAP

Questions # 155:

How does Cisco Workload Optimization Manager help mitigate application performance issues?

Options:

A.

It deploys an AWS Lambda system

B.

It automates resource resizing

C.

It optimizes a flow path

D.

It sets up a workload forensic score

Questions # 156:

A hacker initiated a social engineering attack and stole username and passwords of some users within a company. Which product should be used as a solution to this problem?

Options:

A.

Cisco NGFW

B.

Cisco AnyConnect

C.

Cisco AMP for Endpoints

D.

Cisco Duo

Questions # 157:

How does Cisco Advanced Phishing Protection protect users?

Options:

A.

It validates the sender by using DKIM.

B.

It determines which identities are perceived by the sender

C.

It utilizes sensors that send messages securely.

D.

It uses machine learning and real-time behavior analytics.

Questions # 158:

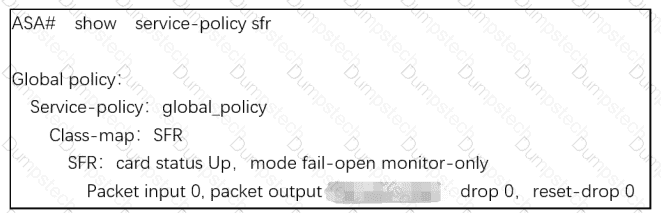
Refer to the exhibit.

Question # 158

What are two indications of the Cisco Firepower Services Module configuration?

(Choose two.)

Options:

A.

The module is operating in IDS mode.

B.

Traffic is blocked if the module fails.

C.

The module fails to receive redirected traffic.

D.

The module is operating in IPS mode.

E.

Traffic continues to flow if the module fails.

Questions # 159:

Which type of algorithm provides the highest level of protection against brute-force attacks?

Options:

A.

PFS

B.

HMAC

C.

MD5

D.

SHA

Questions # 160:

Which technology must be used to implement secure VPN connectivity among company branches over a

private IP cloud with any-to-any scalable connectivity?

Options:

A.

DMVPN

B.

FlexVPN

C.

IPsec DVTI

D.

GET VPN

Questions # 161:

A network engineer is enabling RADIUS CoA on a fleet of Cisco Catalyst switches so that Cisco ISE can quarantine compromised endpoints in real time. To uniquely target an active session for disconnect or reauthorization, Cisco ISE must include IETF attribute 31 to identify the endpoint. Which configuration action must be performed on Cisco ISE to meet the requirement?

Options:

A.

Configure the Calling-Station-ID attribute for CoA session identification.

B.

Apply the Message-Authenticator attribute for endpoint session lookup.

C.

Implement the Acct-Session-ID attribute for matching the active session.

D.

Use the NAS-Port-ID attribute for the CoA disconnect request.

Questions # 162:

Which DevSecOps practice helps reduce vulnerabilities introduced through external open-source components?

Options:

A.

Performing static routing configuration checks

B.

Conducting software composition analysis during builds

C.

Using dynamic routing between Kubernetes clusters

D.

Setting up round-robin DNS resolution for service discovery

Questions # 163:

Which role is a default guest type in Cisco ISE?

Options:

A.

Monthly

B.

Yearly

C.

Contractor

D.

Full-Time

Questions # 164:

Which Cisco DNA Center RESTful PNP API adds and claims a device into a workflow?

Options:

A.

api/v1/fie/config

B.

api/v1/onboarding/pnp-device/import

C.

api/v1/onboarding/pnp-device

D.

api/v1/onboarding/workflow

Questions # 165:

Using Cisco Cognitive Threat Analytics, which platform automatically blocks risky sites, and test unknown sites for hidden advanced threats before allowing users to click them?

Options:

A.

Cisco Identity Services Engine (ISE)

B.

Cisco Enterprise Security Appliance (ESA)

C.

Cisco Web Security Appliance (WSA)

D.

Cisco Advanced Stealthwatch Appliance (ASA)

Viewing page 11 out of 16 pages
Viewing questions 151-165 out of questions