
75only - Ends in 0d 00h 00m 00s - Coupon code = 75only

Pass the Cisco CCNP Security 350-701 Questions and answers with Dumpstech

Exam 350-701 Premium Access

View all detail and faqs for the 350-701 exam

Practice at least 50% of the questions to maximize your chances of passing.
Viewing page 7 out of 16 pages
Viewing questions 91-105 out of questions
Questions # 91:

What is a required prerequisite to enable malware file scanning for the Secure Internet Gateway?

Options:

A.

Enable IP Layer enforcement.

B.

Activate the Advanced Malware Protection license

C.

Activate SSL decryption.

D.

Enable Intelligent Proxy.

Questions # 92:

Which solution is more secure than the traditional use of a username and password and encompasses at least two of the methods of authentication?

Options:

A.

single-sign on

B.

RADIUS/LDAP authentication

C.

Kerberos security solution

D.

multifactor authentication

Questions # 93:

An organization wants to secure users, data, and applications in the cloud. The solution must be API-based and

operate as a cloud-native CASB. Which solution must be used for this implementation?

Options:

A.

Cisco Cloudlock

B.

Cisco Cloud Email Security

C.

Cisco Firepower Next-Generation Firewall

D.

Cisco Umbrella

Questions # 94:

An engineer must configure Cisco AMP for Endpoints so that it contains a list of files that should not be executed by users. These files must not be quarantined. Which action meets this configuration requirement?

Options:

A.

Identity the network IPs and place them in a blocked list.

B.

Modify the advanced custom detection list to include these files.

C.

Create an application control blocked applications list.

D.

Add a list for simple custom detection.

Questions # 95:

Which VMware platform does Cisco ACI integrate with to provide enhanced visibility, provide policy integration and deployment, and implement security policies with access lists?

Options:

A.

VMware APIC

B.

VMwarevRealize

C.

VMware fusion

D.

VMware horizons

Questions # 96:

Which system facilitates deploying microsegmentation and multi-tenancy services with a policy-based container?

Options:

A.

SDLC

B.

Docker

C.

Lambda

D.

Contiv

Questions # 97:

Which feature requires a network discovery policy on the Cisco Firepower Next Generation Intrusion Prevention

System?

Options:

A.

Security Intelligence

B.

Impact Flags

C.

Health Monitoring

D.

URL Filtering

Questions # 98:

What is an attribute of the DevSecOps process?

Options:

A.

mandated security controls and check lists

B.

security scanning and theoretical vulnerabilities

C.

development security

D.

isolated security team

Questions # 99:

Which method must be used to connect Cisco Secure Workload to external orchestrators at a client site when the client does not allow incoming connections?

Options:

A.

source NAT

B.

reverse tunnel

C.

GRE tunnel

D.

destination NAT

Questions # 100:

Which Cisco security solution protects remote users against phishing attacks when they are not connected to

the VPN?

Options:

A.

Cisco Stealthwatch

B.

Cisco Umbrella

C.

Cisco Firepower

D.

NGIPS

Questions # 101:

Which VPN technology can support a multivendor environment and secure traffic between sites?

Options:

A.

SSL VPN

B.

GET VPN

C.

FlexVPN

D.

DMVPN

Questions # 102:

A network engineer must distribute an operating system image to a network device and activate the image on that device by using the Cisco Catalyst Center API. Which two API requests perform the required operations? (Choose two.)

Options:

A.

POST /dna/intent/api/v1/image/distribution

B.

POST /dna/intent/api/v1/onboarding/pnp-device/import

C.

POST /dna/intent/api/v1/image/activation/device

D.

POST /dna/intent/api/v1/network/{site_id}

E.

POST /dna/intent/api/v1/template-programmer/project/{project_id}/template

Questions # 103:

Which type of API is being used when a security application notifies a controller within a software-defined network architecture about a specific security threat?
Options:

A.

westbound AP

B.

southbound API

C.

northbound API

D.

eastbound API

Questions # 104:

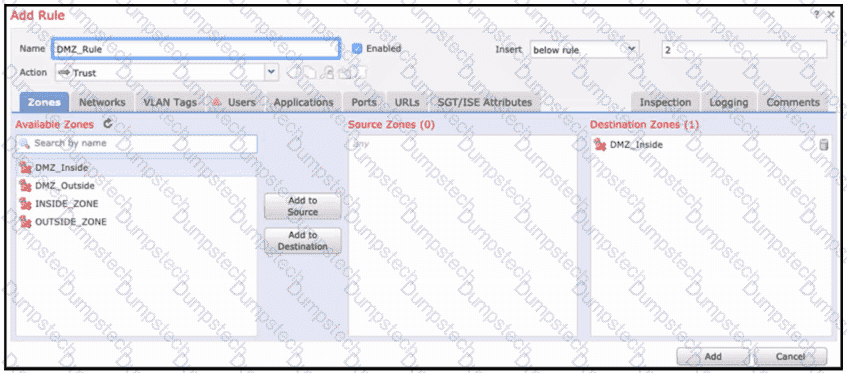
Question # 104

Refer to the exhibit. When configuring this access control rule in Cisco FMC, what happens with the traffic destined to the DMZ_inside zone once the configuration is deployed?

Options:

A.

All traffic from any zone will be allowed to the DMZ_inside zone only after inspection.

B.

No traffic will be allowed through to the DMZ_inside zone regardless of if it ' s trusted or not.

C.

No traffic will be allowed through to the DMZ_inside zone unless it ' s already trusted.

D.

All traffic from any zone to the DMZ_inside zone will be permitted with no further inspection.

Questions # 105:

A logistics company issues corporate laptops that must automatically establish a Cisco Secure Client VPN tunnel whenever users are outside the office and connected to an untrusted external network. Cisco Secure Firewall Threat Defense is the VPN headend and is already configured with remote-access profiles, address pools, and a PKI that distributes both machine and user certificates to endpoints. Management requires the tunnel to come up unattended before any user signs in to a laptop. Device-based authentication must be used, and the client must distinguish the corporate LAN from outside networks. The VPN must be connected when a user is outside the corporate network. Which configuration action must be performed to meet the requirements?

Options:

A.

Configure a Management VPN tunnel with user-certificate authentication for unattended connectivity.

B.

Configure Trusted Network Detection and Start Before Login with machine-certificate authentication for the client.

C.

Configure Trusted Network Detection using cached domain credentials for client authentication.

D.

Implement Start Before Login paired with user-certificate authentication in the profile.

Viewing page 7 out of 16 pages
Viewing questions 91-105 out of questions