75only - Ends in 0d 00h 00m 00s - Coupon code = 75only

Pass the Cisco CCNP Security 350-701 Questions and answers with Dumpstech

Exam 350-701 Premium Access

View all detail and faqs for the 350-701 exam

Practice at least 50% of the questions to maximize your chances of passing.
Viewing page 3 out of 16 pages
Viewing questions 31-45 out of questions
Questions # 31:

Which Cisco solution does Cisco Umbrella integrate with to determine if a URL is malicious?

Options:

A.

AMP

B.

AnyConnect

C.

DynDNS

D.

Talos

Questions # 32:

An administrator has been tasked with configuring the Cisco Secure Email Gateway to ensure there are no viruses before quarantined emails are delivered. In addition, delivery of mail from known bad mail servers must be prevented. Which two actions must be taken in order to meet these requirements? (Choose two.)

Options:

A.

Deploy the Secure Email Gateway in the DMZ.

B.

Use outbreak filters from Cisco Talos.

C.

Configure a recipient access table.

D.

Enable a message tracking service.

E.

Scan quarantined emails using AntiVirus signatures.

Questions # 33:

What is a capability of a Trojan horse on a computer system?

Options:

A.

It replicates itself into other programs.

B.

It disguises itself as a legitimate program.

C.

It inserts its own code when legitimate programs are executed.

D.

It enables access to restricted areas without being detected.

Questions # 34:

An organization is trying to improve their Defense in Depth by blocking malicious destinations prior to a

connection being established. The solution must be able to block certain applications from being used within the network. Which product should be used to accomplish this goal?

Options:

A.

Cisco Firepower

B.

Cisco Umbrella

C.

ISE

D.

AMP

Questions # 35:

In which two customer environments is the Cisco Secure Web Appliance Virtual connector traffic direction method selected? (Choose two.)

Options:

A.

Customer needs to support roaming users.

B.

Customer does not own Cisco hardware and needs Transparent Redirection (WCCP).

C.

Customer owns ASA Appliance and Virtual Form Factor is required.

D.

Customer does not own Cisco hardware and needs Explicit Proxy.

E.

Customer owns ASA Appliance and SSL Tunneling is required.

Questions # 36:

An engineer is adding a Cisco router to an existing environment. NTP authentication is configured on all devices in the environment with the command ntp authentication-key 1 md5 Clsc427128380. There are two routers on the network that are configured as NTP servers for redundancy, 192.168.1.110 and 192.168.1.111. 192.168.1.110 is configured as the authoritative time source. What command must be configured on the new router to use 192.168.1.110 as its primary time source without the new router attempting to offer time to existing devices?

Options:

A.

ntp server 192.168.1.110 primary key 1

B.

ntp peer 192.168.1.110 prefer key 1

C.

ntp server 192.168.1.110 key 1 prefer

D.

ntp peer 192.168.1.110 key 1 primary

Questions # 37:

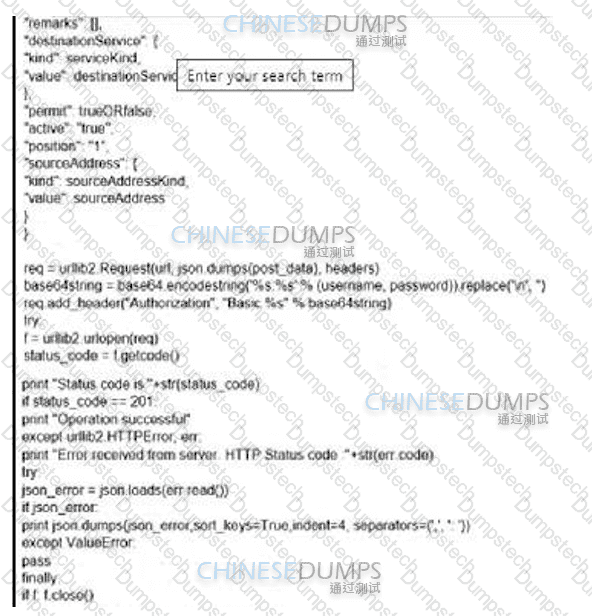
Refer to the exhibit.

Question # 37

What is the function of the Python script code snippet for the Cisco ASA REST API?

Options:

A.

adds a global rule into policies

B.

changes the hostname of the Cisco ASA

C.

deletes a global rule from policies

D.

obtains the saved configuration of the Cisco ASA firewall

Questions # 38:

A pharmaceutical research facility has implemented a “Clean Room” network segment to protect sensitive research data and automated manufacturing equipment. Strict compliance requirements mandate that all network traffic logs from the Cisco Secure Firewall serving the segment be forwarded to Splunk for auditing. A Splunk Universal Forwarder is deployed locally on the log-collection servers to monitor syslog files. The engineer must configure the Universal Forwarder to monitor the local syslog files and assign a specific source type for proper ingestion into Splunk. Which stanza configuration must be used to meet the requirements?

Options:

A.

inputs.conf using [monitor:///var/log/syslog]

B.

server.conf using [monitor:///syslog]

C.

props.conf using [syslog]

D.

outputs.conf using [tcpout]

Questions # 39:

What is an advantage of network telemetry over SNMP pulls?

Options:

A.

accuracy

B.

encapsulation

C.

security

D.

scalability

Questions # 40:

When a Cisco Secure Web Appliance checks a web request, what occurs if it is unable to match a user-defined policy?

Options:

A.

It applies the next identification profile policy.

B.

It applies the advanced policy.

C.

It applies the global policy.

D.

It blocks the request.

Questions # 41:

What are two characteristics of the RESTful architecture used within Cisco DNA Center? (Choose two.)

Options:

A.

REST uses methods such as GET, PUT, POST, and DELETE.

B.

REST codes can be compiled with any programming language.

C.

REST is a Linux platform-based architecture.

D.

The POST action replaces existing data at the URL path.

E.

REST uses HTTP to send a request to a web service.

Questions # 42:

An engineer recently completed the system setup on a Cisco WSA Which URL information does the system send to SensorBase Network servers?

Options:

A.

Summarized server-name information and MD5-hashed path information

B.

complete URL,without obfuscating the path segments

C.

URL information collected from clients that connect to the Cisco WSA using Cisco AnyConnect

D.

none because SensorBase Network Participation is disabled by default

Questions # 43:

What are the two types of managed Intercloud Fabric deployment models? (Choose two.)

Options:

A.

Public managed

B.

Service Provider managed

C.

Enterprise managed

D.

User managed

E.

Hybrid managed

Questions # 44:

Which Cisco WSA feature supports access control using URL categories?

Options:

A.

transparent user identification

B.

SOCKS proxy services

C.

web usage controls

D.

user session restrictions

Questions # 45:

With Cisco AMP for Endpoints, which option shows a list of all files that have been executed in your

environment?

Options:

A.

Prevalence

B.

File analysis

C.

Detections

D.

Vulnerable software

E.

Threat root cause

Viewing page 3 out of 16 pages
Viewing questions 31-45 out of questions