75only - Ends in 0d 00h 00m 00s - Coupon code = 75only

Pass the Cisco CCNP Security 350-701 Questions and answers with Dumpstech

Exam 350-701 Premium Access

View all detail and faqs for the 350-701 exam

Practice at least 50% of the questions to maximize your chances of passing.
Viewing page 4 out of 16 pages
Viewing questions 46-60 out of questions
Questions # 46:

What are two advantages of using Cisco Any connect over DMVPN? (Choose two)

Options:

A.

It provides spoke-to-spoke communications without traversing the hub

B.

It allows different routing protocols to work over the tunnel

C.

It allows customization of access policies based on user identity

D.

It allows multiple sites to connect to the data center

E.

It enables VPN access for individual users from their machines

Questions # 47:

A security policy administrator configures a Cisco Secure Access SIA DNS policy to block all social media categories for the Marketing Active Directory group. While testing from one of the user machines, access to the domain https://socialmediaexample.org is allowed. When searching for this domain in User Activity Search, no queries for that specific domain are returned. Consider these facts:

    The test user is part of the Marketing Active Directory group.

    The domain socialmediaexample.org belongs to the social media category.

    The user is configured with the Umbrella Roaming Client for DNS redirection.

    All other social media websites are properly blocked for the same user and match the correct policy.

Which configuration must the administrator implement in Cisco Secure Access to meet the requirement?
Options:

A.

Enable HTTPS inspection in the web policy because this is an HTTPS site.

B.

Add socialmediaexample.org to the External Domains list.

C.

Enable the intelligent proxy to identify this domain properly.

D.

Add socialmediaexample.org to the Internal Domains list.

Questions # 48:

Question # 48

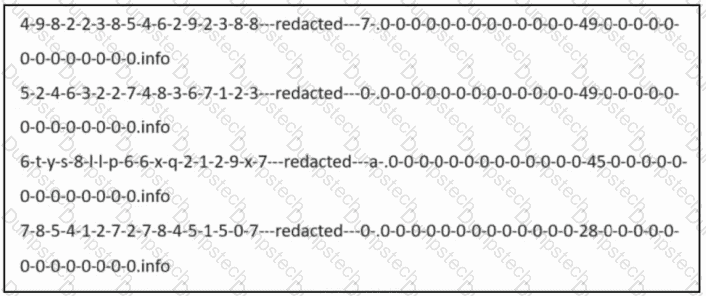
Refer to the exhibit. Consider that any feature of DNS requests, such as the length of the domain name and the number of subdomains, can be used to construct models of expected behavior to which observed values can be compared. Which type of malicious attack are these values associated with?

Options:

A.

W32/AutoRun worm

B.

HeartBleed SSL Bug

C.

Spectre Worm

D.

Eternal Blue Windows

Questions # 49:

What is the purpose of CA in a PKI?

Options:

A.

To issue and revoke digital certificates

B.

To validate the authenticity of a digital certificate

C.

To create the private key for a digital certificate

D.

To certify the ownership of a public key by the named subject

Questions # 50:

Which feature is configured for managed devices in the device platform settings of the Firepower Management

Center?

Options:

A.

quality of service

B.

time synchronization

C.

network address translations

D.

intrusion policy

Questions # 51:

What is the purpose of the Cisco Endpoint loC feature?

Options:

A.

It provides stealth threat prevention.

B.

lt is a signature-based engine.

C.

lt is an incident response tool

D.

It provides precompromise detection.

Questions # 52:

Which service allows a user export application usage and performance statistics with Cisco Application Visibility

and control?

Options:

A.

SNORT

B.

NetFlow

C.

SNMP

D.

802.1X

Questions # 53:

How does DNS Tunneling exfiltrate data?

Options:

A.

An attacker registers a domain that a client connects to based on DNS records and sends malware throughthat connection.

B.

An attacker opens a reverse DNS shell to get into the client’s system and install malware on it.

C.

An attacker uses a non-standard DNS port to gain access to the organization’s DNS servers in order topoison the resolutions.

D.

An attacker sends an email to the target with hidden DNS resolvers in it to redirect them to a maliciousdomain.

Questions # 54:

Which technology limits communication between nodes on the same network segment to individual applications?

Options:

A.

serverless infrastructure

B.

microsegmentation

C.

SaaS deployment

D.

machine-to-machine firewalling

Questions # 55:

How does Cisco AMP for Endpoints provide next-generation protection?

Options:

A.

It encrypts data on user endpoints to protect against ransomware.

B.

It leverages an endpoint protection platform and endpoint detection and response.

C.

It utilizes Cisco pxGrid, which allows Cisco AMP to pull threat feeds from threat intelligence centers.

D.

It integrates with Cisco FTD devices.

Questions # 56:

What is a description of microsegmentation?

Options:

A.

Environments apply a zero-trust model and specify how applications on different servers or containers can communicate

B.

Environments deploy a container orchestration platform, such as Kubernetes, to manage the application delivery

C.

Environments implement private VLAN segmentation to group servers with similar applications.

D.

Environments deploy centrally managed host-based firewall rules on each server or container

Questions # 57:

An organization configures Cisco Umbrella to be used for its DNS services. The organization must be able to block traffic based on the subnet that the endpoint is on but it sees only the requests from its public IP address instead of each internal IP address. What must be done to resolve this issue?

Options:

A.

Set up a Cisco Umbrella virtual appliance to internally field the requests and see the traffic of each IP address

B.

Use the tenant control features to identify each subnet being used and track the connections within theCisco Umbrella dashboard

C.

Install the Microsoft Active Directory Connector to give IP address information stitched to the requests in the Cisco Umbrella dashboard

D.

Configure an internal domain within Cisco Umbrella to help identify each address and create policy from the domains

Questions # 58:

Which solution stops unauthorized access to the system if a user ' s password is compromised?

Options:

A.

VPN

B.

MFA

C.

AMP

D.

SSL

Questions # 59:

A security test performed on one of the applications shows that user input is not validated. Which security vulnerability is the application more susceptible to because of this lack of validation?

Options:

A.

denial -of-service

B.

cross-site request forgery

C.

man-in-the-middle

D.

SQL injection

Questions # 60:

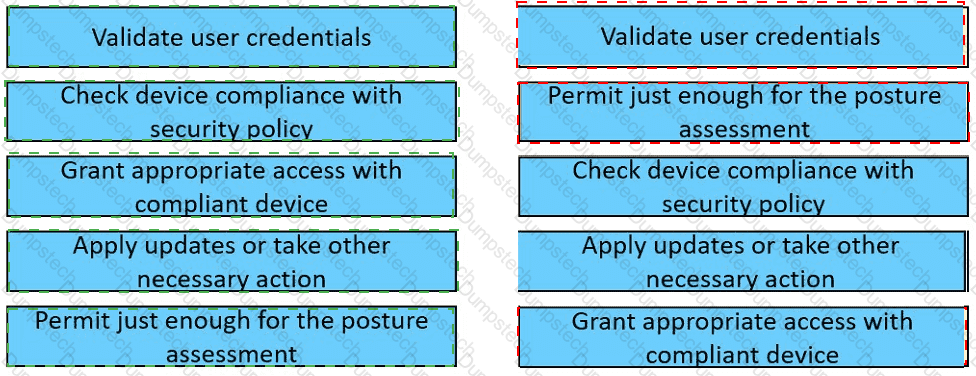
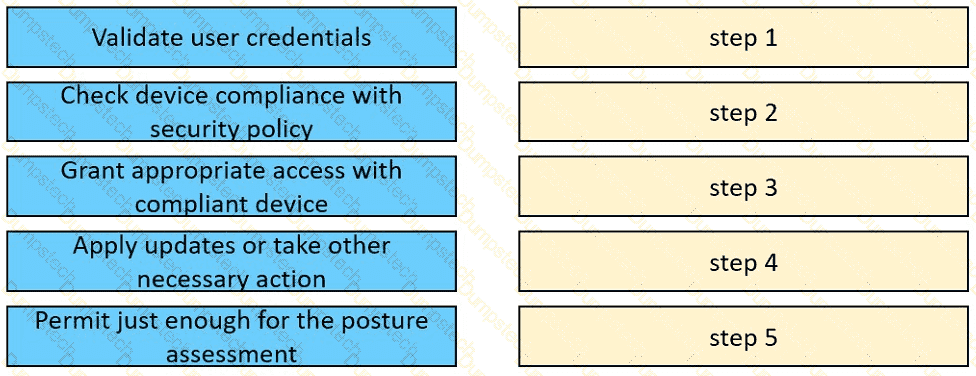
Drag and drop the posture assessment flow actions from the left into a sequence on the right.
Question # 60

Options:

Viewing page 4 out of 16 pages
Viewing questions 46-60 out of questions