75only - Ends in 0d 00h 00m 00s - Coupon code = 75only

Pass the Cisco CCNP Security 350-701 Questions and answers with Dumpstech

Exam 350-701 Premium Access

View all detail and faqs for the 350-701 exam

Practice at least 50% of the questions to maximize your chances of passing.
Viewing page 9 out of 16 pages
Viewing questions 121-135 out of questions
Questions # 121:

Which solution is made from a collection of secure development practices and guidelines that developers must follow to build secure applications?

Options:

A.

AFL

B.

Fuzzing Framework

C.

Radamsa

D.

OWASP

Questions # 122:

An engineer must configure AsyncOS for Cisco Secure Web Appliance to push log files to a syslog server using the SCP retrieval method. Drag and drop the steps from the left into the sequence on the right to complete the configuration.
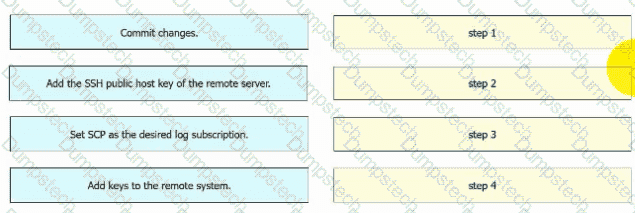
Question # 122

Options:

Questions # 123:

Drag and drop the VPN functions from the left onto the descriptions on the right.
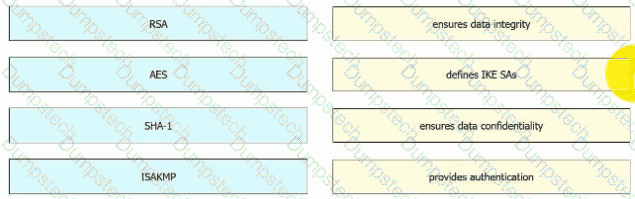
Question # 123

Options:

Questions # 124:

What is the most commonly used protocol for network telemetry?

Options:

A.

SMTP

B.

SNMP

C.

TFTP

D.

NctFlow

Questions # 125:

Which protocol does the BYOD component in Cisco ISE use to obtain a unique device certificate from an internal CA?

Options:

A.

CMP

B.

SCEP

C.

SFTP

D.

OCSP

Questions # 126:

A security policy administrator configures a Cisco Secure Access SIA DNS policy to block all social media categories for the Marketing Active Directory group. While testing from one of the user machines, access to the domain https://socialmediaexample.org is allowed. When searching for this domain in User Activity Search, no queries for that specific domain are returned. Consider these facts:

    The test user is part of the Marketing Active Directory group.

    The domain socialmediaexample.org belongs to the social media category.

    The user is configured with the Umbrella Roaming Client for DNS redirection.

    All other social media websites are properly blocked for the same user and match the correct policy.

Which configuration must the administrator implement in Cisco Secure Access to meet the requirement?

Options:

A.

Enable HTTPS inspection in the web policy because this is an HTTPS site.

B.

Add socialmediaexample.org to the External Domains list.

C.

Enable the intelligent proxy to identify this domain properly.

D.

Add socialmediaexample.org to the Internal Domains list.

Questions # 127:

How does Cisco Umbrella archive logs to an enterprise owned storage?

Options:

A.

by using the Application Programming Interface to fetch the logs

B.

by sending logs via syslog to an on-premises or cloud-based syslog server

C.

by the system administrator downloading the logs from the Cisco Umbrella web portal

D.

by being configured to send logs to a self-managed AWS S3 bucket

Questions # 128:

Which ASA deployment mode can provide separation of management on a shared appliance?

Options:

A.

DMZ multiple zone mode

B.

transparent firewall mode

C.

multiple context mode

D.

routed mode

Questions # 129:

What are two benefits of workload security? (Choose two.)

Options:

A.

Tracked application security

B.

Automated patching

C.

Reduced attack surface

D.

Scalable security policies

E.

Workload modeling

Questions # 130:

What is a key difference between Cisco Firepower and Cisco ASA?

Options:

A.

Cisco ASA provides access control while Cisco Firepower does not.

B.

Cisco Firepower provides identity-based access control while Cisco ASA does not.

C.

Cisco Firepower natively provides intrusion prevention capabilities while Cisco ASA does not.

D.

Cisco ASA provides SSL inspection while Cisco Firepower does not.

Questions # 131:

What is a description of microsegmentation?

Options:

A.

Environments deploy a container orchestration platform, such as Kubernetes, to manage the application delivery.

B.

Environments apply a zero-trust model and specify how applications on different servers or containers can communicate.

C.

Environments deploy centrally managed host-based firewall rules on each server or container.

D.

Environments implement private VLAN segmentation to group servers with similar applications.

Questions # 132:

An engineer enabled SSL decryption for Cisco Umbrella intelligent proxy and needs to ensure that traffic is inspected without alerting end-users.

Options:

A.

Upload the organization root CA to the Umbrella admin portal

B.

Modify the user ' s browser settings to suppress errors from Umbrella.

C.

Restrict access to only websites with trusted third-party signed certificates.

D.

Import the Umbrella root CA into the trusted root store on the user ' s device.

Questions # 133:

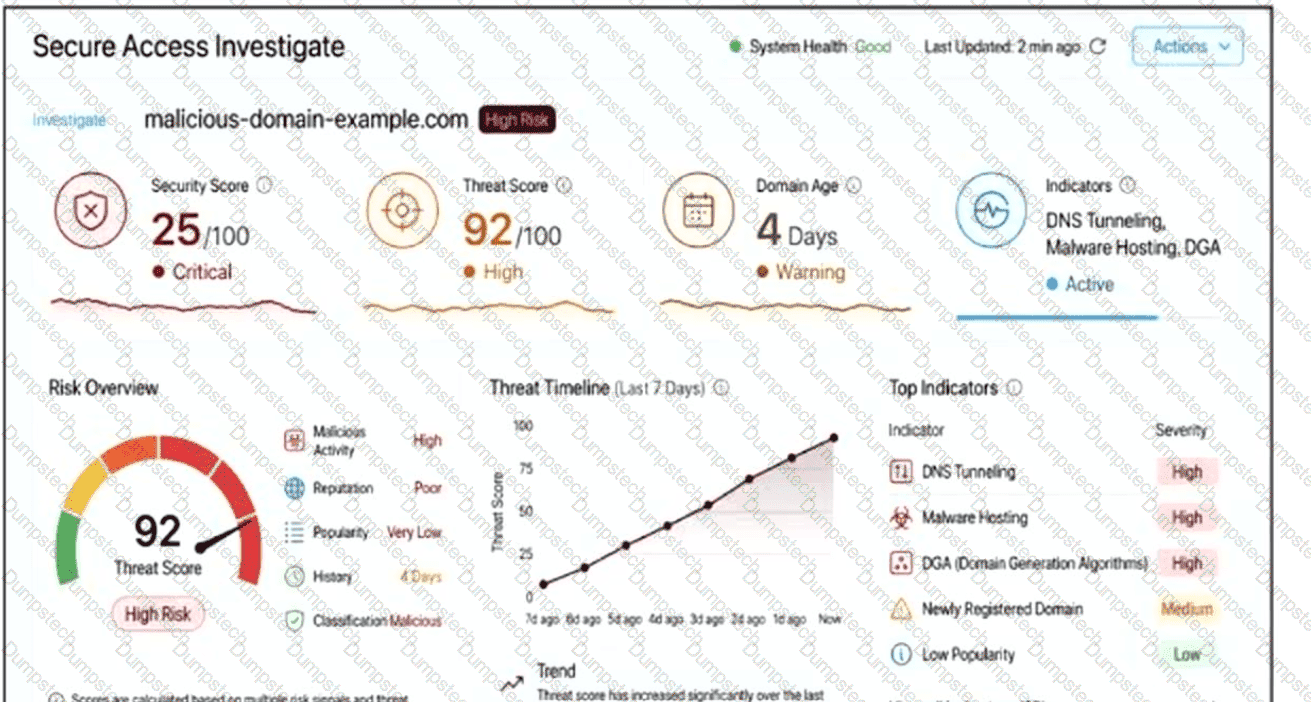
Refer to the exhibit.

Question # 133

What conclusion should an administrator draw about the URL malicious-domain-example.com?

Options:

A.

The domain is blocked solely because it is newly registered, regardless of the Threat Score.

B.

The domain is a legacy site that has been compromised, as indicated by its domain age.

C.

The domain is safe because its Security Score is 25/100.

D.

The high Threat Score together with DNS tunneling, malware hosting, and DGA indicators shows active malicious behavior.

Questions # 134:

Which two actions does the Cisco ISE posture module provide that ensures endpoint security? (Choose two.)

Options:

A.

A centralized management solution is deployed.

B.

Patch management remediation is performed.

C.

The latest antivirus updates are applied before access is allowed.

D.

Assignments to endpoint groups are made dynamically, based on endpoint attributes.

E.

Endpoint supplicant configuration is deployed.

Questions # 135:

Which two cryptographic algorithms are used with IPsec? (Choose two)

Options:

A.

AES-BAC

B.

AES-ABC

C.

HMAC-SHA1/SHA2

D.

Triple AMC-CBC

E.

AES-CBC

Viewing page 9 out of 16 pages
Viewing questions 121-135 out of questions