75only - Ends in 0d 00h 00m 00s - Coupon code = 75only

Pass the Cisco CCNP Security 350-701 Questions and answers with Dumpstech

Exam 350-701 Premium Access

View all detail and faqs for the 350-701 exam

Practice at least 50% of the questions to maximize your chances of passing.
Viewing page 12 out of 16 pages
Viewing questions 166-180 out of questions
Questions # 166:

A network administrator is using the Cisco ESA with AMP to upload files to the cloud for analysis. The network

is congested and is affecting communication. How will the Cisco ESA handle any files which need analysis?

Options:

A.

AMP calculates the SHA-256 fingerprint, caches it, and periodically attempts the upload.

B.

The file is queued for upload when connectivity is restored.

C.

The file upload is abandoned.

D.

The ESA immediately makes another attempt to upload the file.

Questions # 167:

Why should organizations migrate to an MFA strategy for authentication?

Options:

A.

Single methods of authentication can be compromised more easily than MFA.

B.

Biometrics authentication leads to the need for MFA due to its ability to be hacked easily.

C.

MFA methods of authentication are never compromised.

D.

MFA does not require any piece of evidence for an authentication mechanism.

Questions # 168:

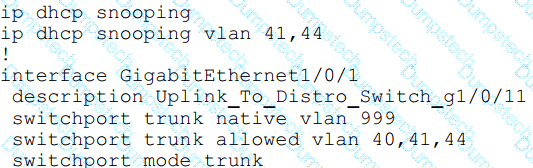
Refer to the exhibit.

Question # 168

An organization is using DHCP Snooping within their network. A user on VLAN 41 on a new switch is

complaining that an IP address is not being obtained. Which command should be configured on the switch

interface in order to provide the user with network connectivity?

Options:

A.

ip dhcp snooping verify mac-address

B.

ip dhcp snooping limit 41

C.

ip dhcp snooping vlan 41

D.

ip dhcp snooping trust

Questions # 169:

Which algorithm provides encryption and authentication for data plane communication?

Options:

A.

AES-GCM

B.

SHA-96

C.

AES-256

D.

SHA-384

Questions # 170:

What are two ways a network administrator transparently identifies users using Active Directory on the Cisco WSA? (Choose two.) The eDirectory client must be installed on each client workstation.

Options:

A.

Create NTLM or Kerberos authentication realm and enable transparent user identification

B.

Deploy a separate Active Directory agent such as Cisco Context Directory Agent.

C.

Create an LDAP authentication realm and disable transparent user identification.

D.

Deploy a separate eDirectory server: the client IP address is recorded in this server

Questions # 171:

Which Talos reputation center allows you to track the reputation of IP addresses for email and web traffic?

Options:

A.

IP Blacklist Center

B.

File Reputation Center

C.

AMP Reputation Center

D.

IP and Domain Reputation Center

Questions # 172:

A security engineer requires social-media websites to be blocked through Cisco Secure Firewall Threat Defense. Which configuration action must the engineer apply to meet the requirement?

Options:

A.

Enable global settings with default URL filtering.

B.

Configure a file policy in an access control policy.

C.

Apply web filtering in an access control policy.

D.

Block the social-media URL category in the destination-network condition of an access control rule.

Questions # 173:

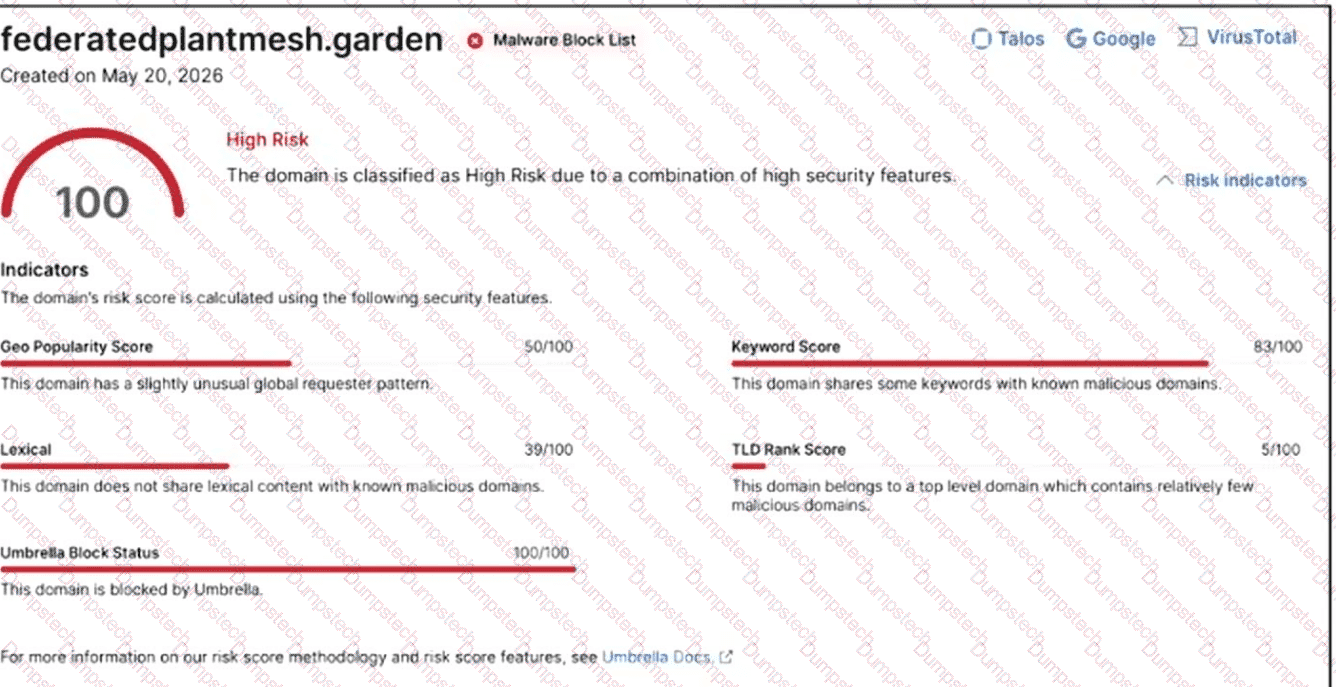
Refer to the exhibit.

Question # 173

A threat analyst is investigating the domain federatedplantmesh.garden after it appeared in DNS logs from several roaming users. In the Cisco Secure Access Investigate dashboard, the analyst notes that several individual indicators, including Lexical, TLD, and Geo Popularity, are not strongly elevated, yet the overall Risk Score is 100. What is occurring?

Options:

A.

The overall score of 100 is inconsistent and likely a dashboard-rendering error; the domain must be queried again before the classification is trusted.

B.

The infrastructure fields are blank, but the Umbrella Block Status of 100/100 and the malware security category identify the non-resolving domain as high risk.

C.

The Keyword Score of 83 is the only elevated indicator driving the overall score, and the classification is invalid unless confirmed through the Dispute Categorization link.

D.

The Dispute Categorization link means that the malware classification is contested, and the blank IP and ASN fields confirm that the domain has no active threat infrastructure.

Questions # 174:

Which two application layer preprocessors are used by Firepower Next Generation Intrusion Prevention

System? (Choose two)

Options:

A.

packet decoder

B.

SIP

C.

modbus

D.

inline normalization

E.

SSL

Questions # 175:

Which policy is used to capture host information on the Cisco Firepower Next Generation Intrusion Prevention

System?

Options:

A.

Correlation

B.

Intrusion

C.

Access Control

D.

Network Discovery

Questions # 176:

Based on the NIST 800-145 guide, which cloud architecture may be owned, managed, and operated by one or more of the organizations in the community, a third party, or some combination of them, and it may exist on or off premises?

Options:

A.

hybrid cloud

B.

private cloud

C.

public cloud

D.

community cloud

Questions # 177:

Which type of data exfiltration technique encodes data in outbound DNS requests to specific servers

and can be stopped by Cisco Umbrella?

Options:

A.

DNS tunneling

B.

DNS flood attack

C.

cache poisoning

D.

DNS hijacking

Questions # 178:

Which two Cisco ISE components must be configured for BYOD? (Choose two.)

Options:

A.

local WebAuth

B.

central WebAuth

C.

null WebAuth

D.

guest

E.

dual

Questions # 179:

What is a benefit of a Cisco Secure Email Gateway Virtual as compared to a physical Secure Email Gateway?

Options:

A.

simplifies the distribution of software updates

B.

provides faster performance

C.

provides an automated setup process

D.

enables the allocation of additional resources

Questions # 180:

A security engineer must configure a Splunk Universal Forwarder to send network traffic logs from Cisco Catalyst switches to a Splunk indexer cluster. Strict compliance requirements require all network traffic logs to be ingested into Splunk as an audit trail. The environment includes thousands of forwarders, and the data must be distributed across all indexers. Which two configuration actions must be performed? (Choose two.)

Options:

A.

Configure outputs.conf with the DNS names and indexing ports of all indexers within the cluster.

B.

Implement a large output queue in outputs.conf and disable automatic load balancing.

C.

Configure the forwarder to write logs to a local file share and schedule a batch job to copy the data into the indexers.

D.

Use a deployment server to push an application containing outputs.conf to all Universal Forwarders.

E.

Configure a single primary indexer in outputs.conf and enable a forced connection.

Viewing page 12 out of 16 pages
Viewing questions 166-180 out of questions