
75only - Ends in 0d 00h 00m 00s - Coupon code = 75only

Pass the Cisco CCNP Security 350-701 Questions and answers with Dumpstech

Exam 350-701 Premium Access

View all detail and faqs for the 350-701 exam

Practice at least 50% of the questions to maximize your chances of passing.
Viewing page 16 out of 16 pages
Viewing questions 226-240 out of questions
Questions # 226:

What must be configured on Cisco Secure Endpoint to create a custom detection tile list to detect and quarantine future files?

Options:

A.

Use the simple custom detection feature and add each detection to the list.

B.

Add a network IP block allowed list to the configuration and add the blocked files.

C.

Create an advanced custom detection and upload the hash of each file

D.

Configure an application control allowed applications list to block the files

Questions # 227:

In which scenario is endpoint-based security the solution?

Options:

A.

inspecting encrypted traffic

B.

device profiling and authorization

C.

performing signature-based application control

D.

inspecting a password-protected archive

Questions # 228:

A network engineer must enable DHCP snooping on the corporate switches only for VLAN 2. Management requires DHCP traffic from unauthorized servers to be dropped. DHCP snooping is already enabled globally, and the uplink interface toward the authorized DHCP server is already trusted. Which configuration command must be applied to meet the requirement?

Options:

A.

ip dhcp snooping trust vlan 2

B.

ip dhcp relay information trusted vlan 2

C.

ip dhcp snooping information option vlan 2

D.

ip dhcp snooping vlan 2

Questions # 229:

Which IPS analysis technique matches traffic against a database of known attack patterns?

Options:

A.

Signature-based detection

B.

Behavioral analytics

C.

Heuristic detection

D.

Anomaly-based detection

Questions # 230:

What is the process of performing automated static and dynamic analysis of files against preloaded

behavioral indicators for threat analysis?

Options:

A.

deep visibility scan

B.

point-in-time checks

C.

advanced sandboxing

D.

advanced scanning

Questions # 231:

Which service allows a user to export application usage and performance statistics with Cisco Application Visibility and Control?

Options:

A.

SNMP

B.

802.1X

C.

NetFlow

D.

SNORT

Questions # 232:

For which two conditions can an endpoint be checked using ISE posture assessment? (Choose two)

Options:

A.

Windows service

B.

computer identity

C.

user identity

D.

Windows firewall

E.

default browser

Questions # 233:

An administrator enables Cisco Threat Intelligence Director on a Cisco FMC. Which process uses STIX and allows uploads and downloads of block lists?

Options:

A.

consumption

B.

sharing

C.

editing

D.

authoring

Questions # 234:

An engineer needs to configure an access control policy rule to always send traffic for inspection without

using the default action. Which action should be configured for this rule?

Options:

A.

monitor

B.

allow

C.

block

D.

trust

Questions # 235:

An organization is implementing URL blocking using Cisco Umbrella. The users are able to go to some sites

but other sites are not accessible due to an error. Why is the error occurring?

Options:

A.

Client computers do not have the Cisco Umbrella Root CA certificate installed.

B.

IP-Layer Enforcement is not configured.

C.

Client computers do not have an SSL certificate deployed from an internal CA server.

D.

Intelligent proxy and SSL decryption is disabled in the policy

Questions # 236:

What is a feature of Cisco NetFlow Secure Event Logging for Cisco ASAs?

Options:

A.

Multiple NetFlow collectors are supported

B.

Advanced NetFlow v9 templates and legacy v5 formatting are supported

C.

Secure NetFlow connections are optimized for Cisco Prime Infrastructure

D.

Flow-create events are delayed

Questions # 237:

What does the Cloudlock Apps Firewall do to mitigate security concerns from an application perspective?

Options:

A.

It allows the administrator to quarantine malicious files so that the application can function, just notmaliciously.

B.

It discovers and controls cloud apps that are connected to a company’s corporate environment.

C.

It deletes any application that does not belong in the network.

D.

It sends the application information to an administrator to act on.

Questions # 238:

Drag and drop the concepts from the left onto the correct descriptions on the right
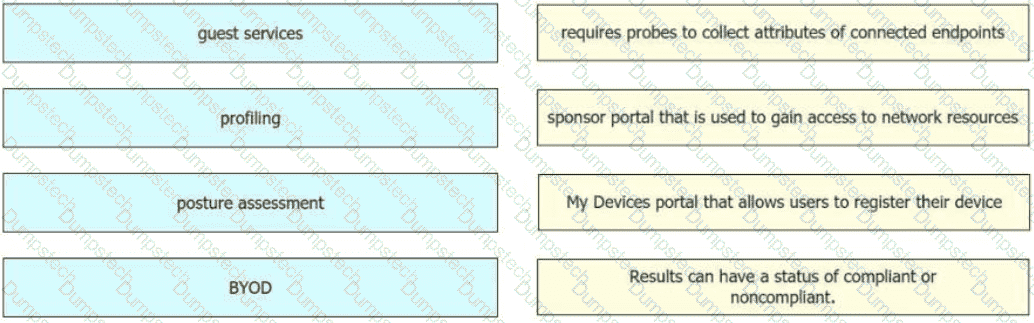
Question # 238

Options:

Questions # 239:

A Cisco Secure Email Gateway network administrator has been tasked to use a newly installed service to help create policy based on the reputation verdict. During testing, it is discovered that the Secure Email Gateway is not dropping files that have an undetermined verdict. What is causing this issue?

Options:

A.

The file has a reputation score that is below the threshold.

B.

The file has a reputation score that is above the threshold.

C.

The policy was created to disable file analysis.

D.

The policy was created to send a message to quarantine instead of drop.

Questions # 240:

Which proxy mode must be used on Cisco WSA to redirect TCP traffic with WCCP?

Options:

A.

transparent

B.

redirection

C.

forward

D.

proxy gateway

Viewing page 16 out of 16 pages
Viewing questions 226-240 out of questions