75only - Ends in 0d 00h 00m 00s - Coupon code = 75only

Pass the Fortinet Network Security Expert NSE5_FSW_AD-7.6 Questions and answers with Dumpstech

Exam NSE5_FSW_AD-7.6 Premium Access

View all detail and faqs for the NSE5_FSW_AD-7.6 exam

Practice at least 50% of the questions to maximize your chances of passing.
Viewing page 4 out of 4 pages
Viewing questions 31-40 out of questions
Questions # 31:

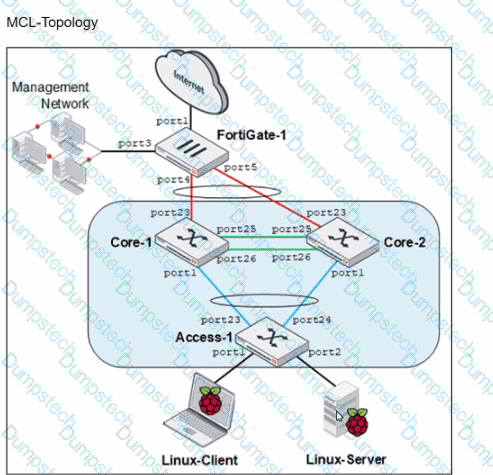
Refer to the exhibit.

Question # 31

Core-1 and Access-1 are managed and authorized by FortiGate-1. which uses port4 as the FortiLink interface. After FortiGate authorizes and manages Core-2. Port1 status becomes STP discarding.

Why is port1 in the discarding state?

Options:

A.

port1 on Core-2 is discarding only management traffic.

B.

Core-1 and Core-2 do not have MCLAG configuration.

C.

Access-1 is the root bridge and can only have one root port.

D.

Core-2 has the lowest bridge priority.

Questions # 32:

(Full question statement start from here)

When you change FortiSwitch management mode fromstandalonetomanaged, what happens to the existing standalone configuration? (Choose one answer)

Options:

A.

FortiSwitch registers to FortiSwitch Cloud to save a copy before managing with FortiGate.

B.

FortiSwitch merges the existing standalone configuration with the default FortiLink configuration.

C.

FortiSwitch saves the standalone configuration and changes to the default FortiLink configuration.

D.

FortiGate automatically saves the existing FortiSwitch configuration during the FortiLink management process.

Questions # 33:

(Full question statement start from here)

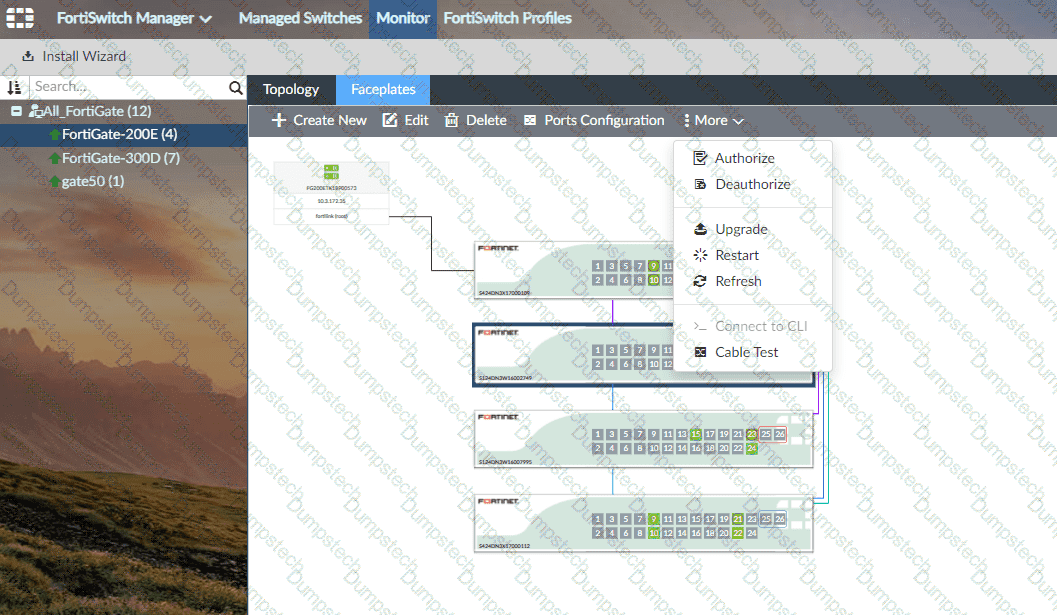
Refer to the exhibit.
Question # 33

Question # 33

Question # 33

Which information does FortiGate use to generate the port details in the FortiSwitch Faceplates view? (Choose one answer)

Options:

A.

The FortiSwitch model

B.

The Cisco Discovery Protocol (CDP) advertisements from FortiSwitch

C.

The LLDP advertisements received from the FortiSwitch

D.

The FortiLink discovery frames sent by FortiSwitch

Questions # 34:

(Full question statement start from here)

What is one key advantage of using a sniffer profile on FortiSwitch compared to using the sniffer command? (Choose one answer)

Options:

A.

It allows packet capture on all switch ports without limitations.

B.

It eliminates the need to use access control lists (ACLs) or port mirroring for analysis.

C.

It automatically filters irrelevant traffic types.

D.

It automatically decrypts SSL/TLS traffic for full packet inspection.

Viewing page 4 out of 4 pages
Viewing questions 31-40 out of questions