Winter Sale Limited Time 75% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code = simple75

Pass the Fortinet NSE 7 Network Security Architect NSE7_FSN_AR-7.6 Questions and answers with Dumpstech

Exam NSE7_FSN_AR-7.6 Premium Access

View all detail and faqs for the NSE7_FSN_AR-7.6 exam

Practice at least 50% of the questions to maximize your chances of passing.
Viewing page 5 out of 6 pages
Viewing questions 41-50 out of questions
Questions # 41:

During the SAML negotiation process, in which section does the Identity Provider (IdP) provide the SAML attributes used in the authentication process to the Service Provider (SP)?

Options:

A.

Bindings HTTP post

B.

Assertion dump

C.

Authentication request

D.

Authentication response

Questions # 42:

Refer to the exhibits,

Question # 42

which show the configuration on FortiGate and partial session information for internet traffic from a user on the internal network. If the priority on route ID 2 were changed from 10 to 0, what would happen to traffic matching that user session? (Choose one answer)

Options:

A.

The session would be deleted, and the client would need to start a new session.

B.

The session would remain in the session table, but its traffic would now egress from both port1 and port2.

C.

The session would remain in the session table, and its traffic would egress from port2.

D.

The session would remain in the session table, and its traffic would egress from port1.

Questions # 43:

Exhibit.

Question # 43

Refer to the exhibit, which shows two entries that were generated in the FSSO collector agent logs.eeeeeeeeeeeeeeeeeeeeeeeeeeeeeeeeeeeeeeeeeeeeeeeeeeeeeeeeeeeeeeeeeeeeeee

What three conclusions can you draw from these log entries? {Choose three.)

Options:

A.

Remote registry is not running on the workstation.

B.

The user ' s status shows as " not verified " in the collector agent.

C.

DNS resolution is unable to resolve the workstation name.

D.

The FortiGate firmware version is not compatible with that of the collector agent.

E.

A firewall is blocking traffic to port 139 and 445.

Questions # 44:

The local OSPF router is unable to establish adjacency with a peer.

Which two things should the administrator do to troubleshoot the issue? (Choose two.)

Options:

A.

Check if both peers have an IP address within the same subnet.

B.

Check if IP protocol 89 is blocked.

C.

Check if TCP port 179 is blocked.

D.

Check if there is an active static route to the peer.

Questions # 45:

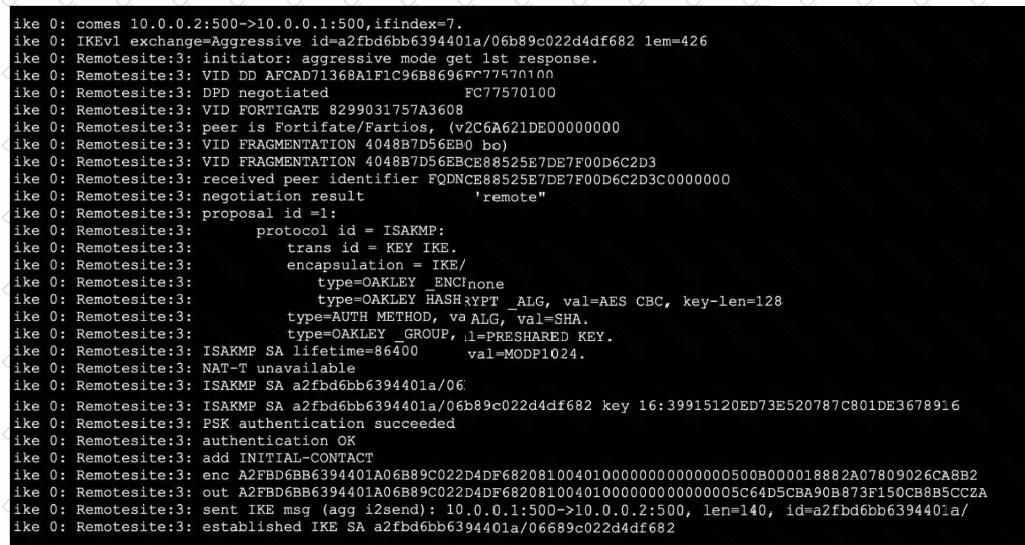
Exhibit.

Question # 45

Refer to the exhibit, which contains partial output from an IKE real-time debug.

Which two statements about this debug output are correct? (Choose two.)

Options:

A.

Perfect Forward Secrecy (PFS) is enabled in the configuration.

B.

The local gateway IP address is 10.0.0.1.

C.

It shows a phase 2 negotiation.

D.

The initiator provided remote as its IPsec peer ID.

Questions # 46:

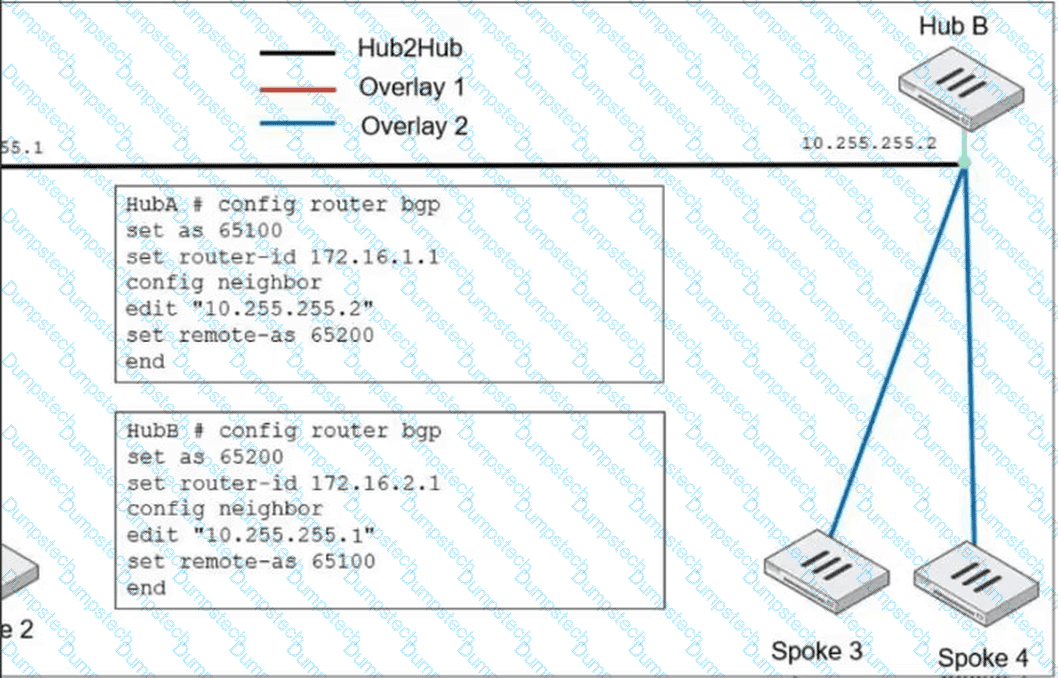
Refer to the exhibit.

Question # 46

An auto-discovery VPN (ADVPN) network is shown.

You must configure an ADVPN using iBGP for each local region and eBGP across regions to connect Overlay 1 with Overlay 2.

Which two options must you configure in the Hub2Hub BGP peering? (Choose two.)

Options:

A.

set next-hop-self enable

B.

set attribute-unchanged next-hop

C.

set ebgp-enforce-multihop enable

D.

set ebgp-enforce-multihop advpn

Questions # 47:

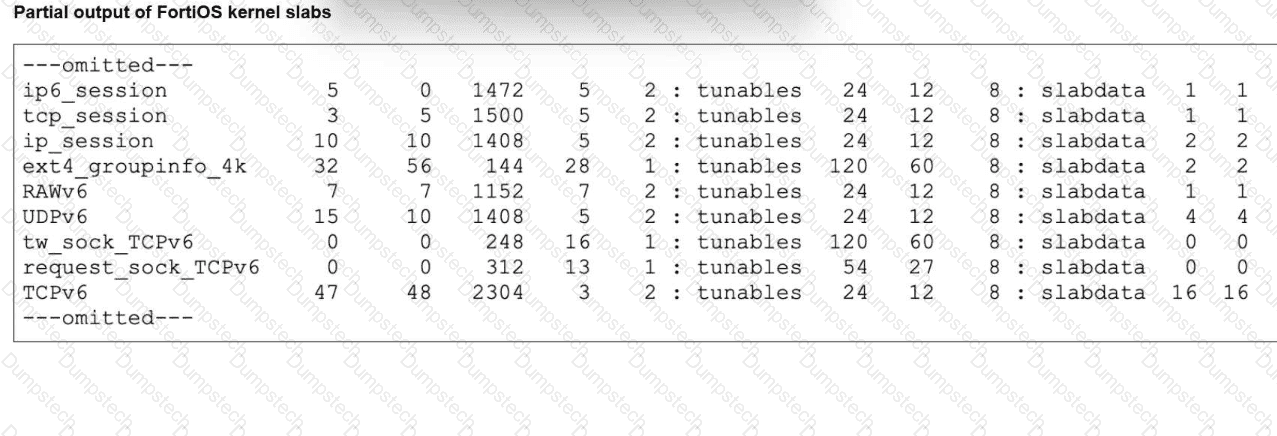
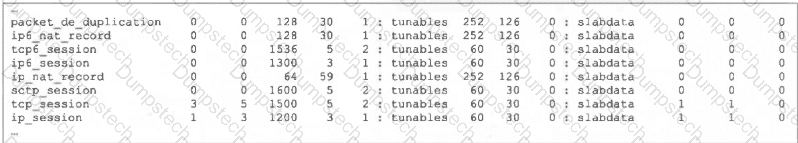
Refer to the exhibit, which shows the partial output of FortiOS kernel slabs.
Question # 47

Which statement is true?

Options:

A.

The total slab size of the sctp_session slab is 0 kB and is associated with the user space.

B.

The total slab size of the ip_session slab is 3600 kB and is associated with the user space.

C.

The total slab size of the ip6_session slab is 1300 kB and is associated with the kernel.

D.

The total slab size of the tcp_session slab is 7500 kB and is associated with the kernel.

Questions # 48:

Refer to the exhibit.

Question # 48

The partial output of FortiOS kernel slabs is shown. Which statement about total slab size is true?
Options:

A.

The total slab size of the ip_session Tlab is 14080 kB and is associated with the user space.

B.

The total slab size of the tcp_session slab is 7500 kB and is associated with the kernel.

C.

The total slab size of the ip6_session slab is 1472 kB and is associated with the kernel.

D.

The total slab size of the UDPv6 slab is 14080 kB and is associated with the user space.

Questions # 49:

Question # 49

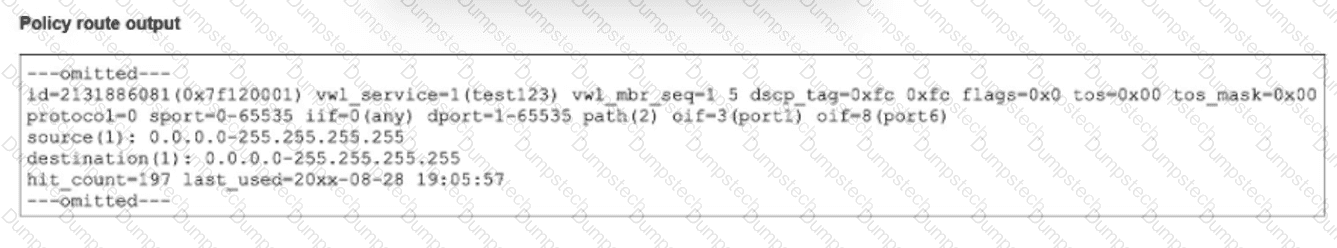
The output of a policy route table entry is shown.

Which type of policy route does the output show?

Options:

A.

A regular policy route, which is not associated with an active static route in the FIB

B.

An ISDB route

C.

An SD-WAN rule

D.

A regular policy route, which is associated with an active static route in the FIB

Questions # 50:

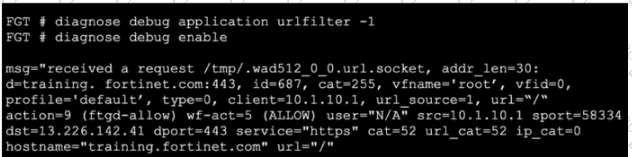
Refer to the exhibit, which shows the output of a real-time debug. Which statement about this output is true? (Choose one answer)
Question # 50

Options:

A.

The server hostname was extracted from the SNI in the client request, or from the CN in the server certificate.

B.

FortiGate found the requested URL in its local cache.

C.

This web request was inspected using the ftgd-allow web filter profile.

D.

The requested URL belongs to category ID 255.

Viewing page 5 out of 6 pages
Viewing questions 41-50 out of questions